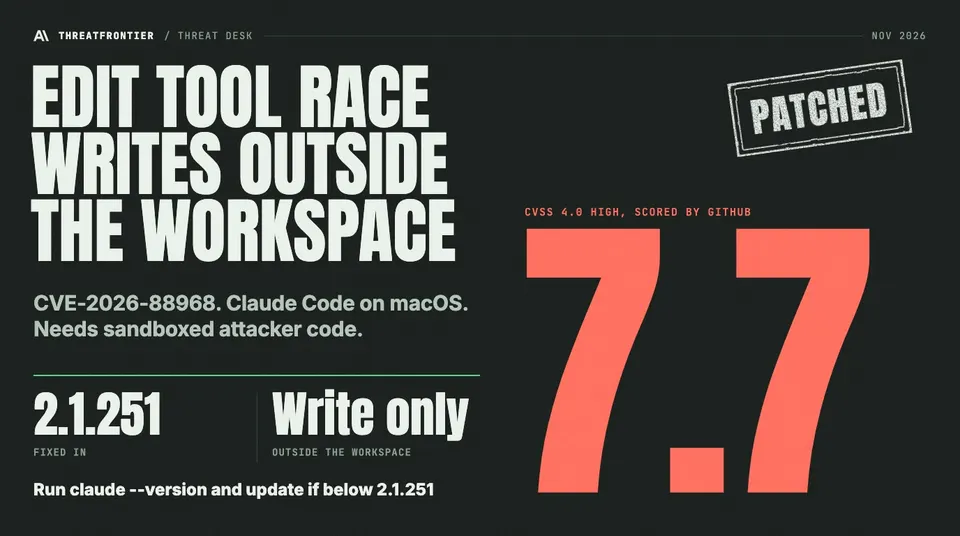
Code already in Claude Code's Bash sandbox could race the Edit tool through a swapped symlink and overwrite user files outside the workspace. Fixed in 2.1.251.
Anthropic has fixed CVE-2026-88968, a race condition in Claude Code's Edit tool on macOS. Code already running inside the Bash sandbox could trick the unsandboxed Edit tool into overwriting a file outside the project. Versions of @anthropic-ai/claude-code before 2.1.251 are affected. GitHub scores it 7.7 (High) on CVSS 4.0.
Who is affected
The advisory covers Claude Code on macOS earlier than 2.1.251. Users on standard auto-update received the fix automatically, according to the advisory. Anyone who updates by hand, or installed through a package manager that does not auto-update, should check their version.
What the flaw is
Claude Code checked Edit-tool targets using point-in-time pathname and symlink resolution that was not bound to the underlying directory inode or a file descriptor. That leaves a gap between the check and the write (CWE-367, time-of-check to time-of-use; also CWE-59, improper link resolution before file access).
On macOS, a process inside the Bash sandbox could atomically swap an in-workspace parent directory for a symlink after validation had passed. The Edit implementation, which runs outside the sandbox, then wrote through the symlink and overwrote an attacker-chosen, user-writable file outside the workspace.
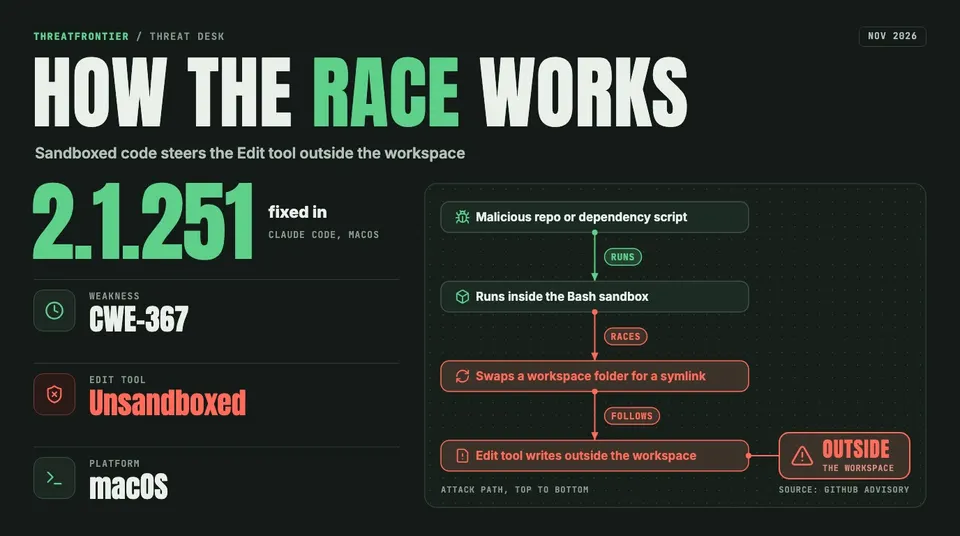
How code inside the sandbox steered the unsandboxed Edit tool before 2.1.251.
Limits of the attack
- It needs attacker-controlled code to already be running in the sandbox. The advisory names a malicious repository or a dependency script as examples.
- It is a write primitive. Neither the advisory nor the NVD record describes a way to read files outside the workspace, so this is not a general sandbox escape for reads.
- The target must be writable by the user running Claude Code.
- The CISA coordinator's SSVC entry in NVD lists exploitation as "none" and automatable as "no".
The CVSS 4.0 vector is AV:N/AC:L/AT:P/PR:N/UI:P/VC:H/VI:H/VA:H, with attack requirements marked present. The score comes from GitHub as CNA; NVD lists the record as "Awaiting Analysis".
Dates
The GitHub advisory page shows publication on 26 October 2026. The NVD record was published on 3 November 2026, so the CVE entry appeared about a week after the advisory.
What to do
Check your version:
claude --version
If it prints anything below 2.1.251, update:
claude update                               # native install
brew upgrade claude-code                    # Homebrew
npm install -g @anthropic-ai/claude-code@latest   # npm
Per Anthropic's setup docs, Homebrew, WinGet, apt, dnf and apk installs do not auto-update. claude doctor shows the last update attempt. The advisory lists no workaround, so upgrading is the remedy. Until then, be cautious about running Claude Code on untrusted repositories, since exploitation depends on hostile code reaching the sandbox.
Credit for the report goes to Sunder Singh (mahoraga007), via HackerOne.