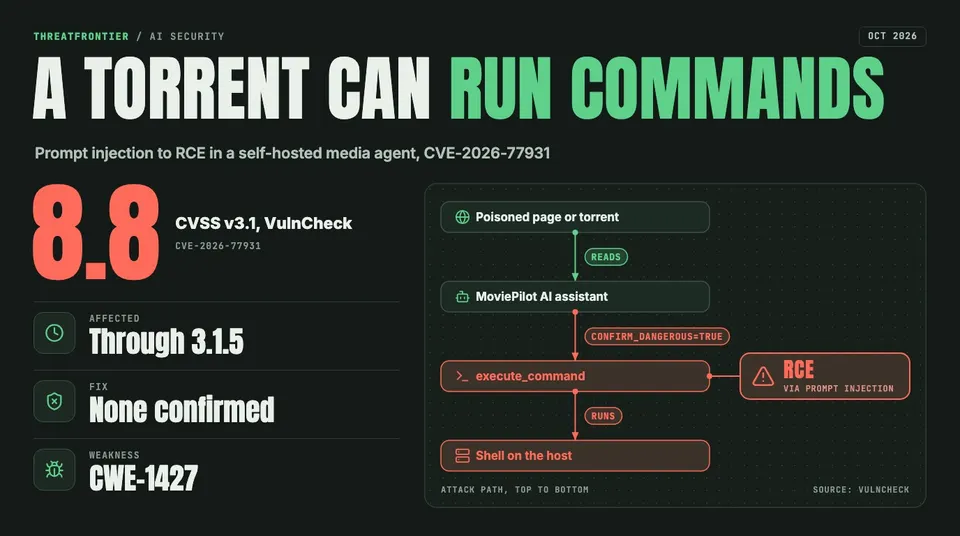
A poisoned web page or torrent can make MoviePilot's AI agent run shell commands on the host. Versions through 3.1.5 are affected and no fix is confirmed.
A prompt-injection flaw in MoviePilot, the self-hosted media automation tool from jxxghp, lets content the AI assistant reads trigger arbitrary shell commands on the host. CVE-2026-77931 affects every version through 3.1.5. VulnCheck rates it 8.8 (CVSS v3.1) and 8.7 (CVSS v4.0). No source we checked names a fixed version.
What happens
The CVE was published on 15 October 2026 by VulnCheck, with a public disclosure date of 12 October. It is classed as CWE-1427, improper neutralization of input used for LLM prompting. Credit goes to Noy Pearl, Michael Sromin and Ophir Dror.
Attackers plant instructions in untrusted content that MoviePilot's agent tools process: web pages fetched by browse_webpage or search_web, and torrent metadata. The injected text makes the model call execute_command with confirm_dangerous set to true. That flag bypasses the validate_command_safety denylist. The call runs in the admin session's context, so the result is remote code execution on the host.
Technical detail
Lasso Security, which wrote up the issue, says execute_command is always offered to the model and that the model can set confirm_dangerous itself, so the safety check is not an independent control. The advisory points to asyncio.create_subprocess_shell in ExecuteCommandTool as the execution path. Lasso says the attack needs no direct access to the instance and no non-default configuration, and that the researchers reproduced it in a proof of concept. It lists no known exploitation. The CVE is not in CISA's KEV catalog, and EPSS is about 1 percent. The v3.1 vector is AV:N/AC:L/PR:N/UI:R: user interaction is needed, in the sense that the assistant must ingest the poisoned content.
Fix status
The VulnCheck, NVD and Lasso records name no patched release. MoviePilot shipped 3.1.6 on 15 October, 3.1.7 on 18 October and 3.1.8 on 19 October. The notes we read for 3.1.6 and 3.1.8 do not mention this issue, and on 21 October the main branch still carries the confirm_dangerous parameter in app/agent/tools/impl/execute_command.py. Treat 3.1.8 as unverified, not as fixed.
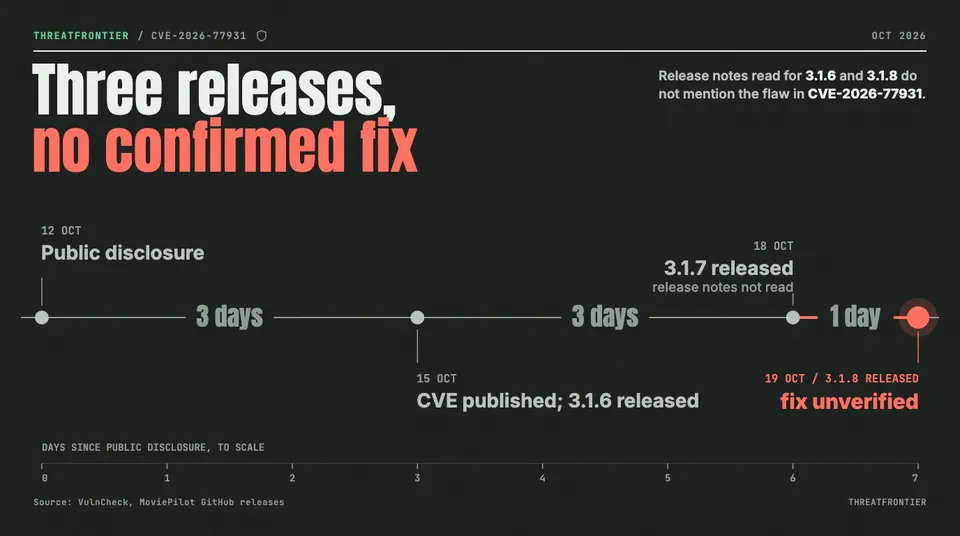
Three releases since disclosure, none confirmed to fix the flaw.
Three releases since disclosure, none confirmed to fix the flaw.
What defenders should do
- Do not let the assistant browse, search or process torrent metadata from untrusted sources while it holds admin rights, until a fix is confirmed.
- Run MoviePilot as a non-root user in a container with no host mounts.
- Lasso's suggested remediation for the vendor: make execute_command, write_file and edit_file opt-in and off by default; require human confirmation for any turn that ingested external content; replace the model-settable confirm_dangerous flag with an allowlist or out-of-band confirmation.
- Watch the MoviePilot releases page and the CVE record for a patched version.