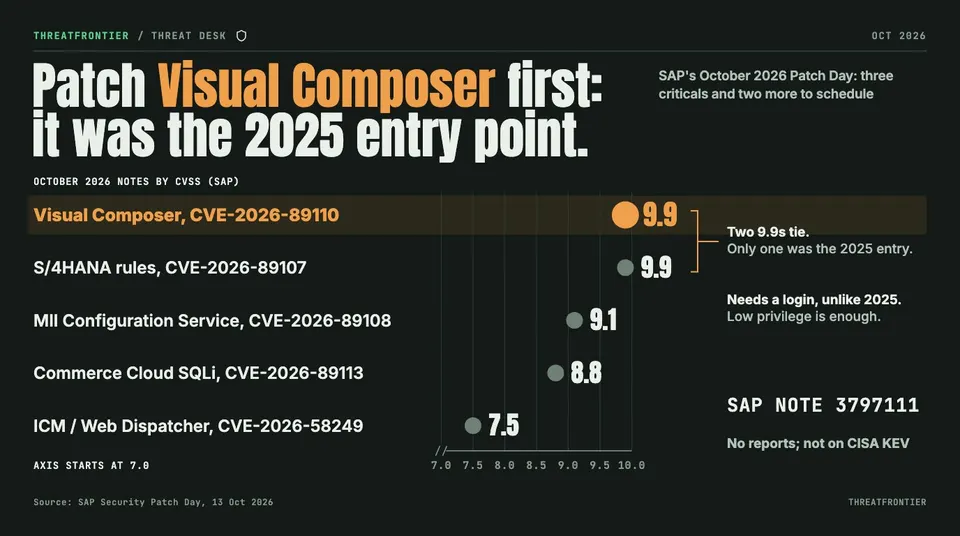
SAP's October 2026 Patch Day fixes a 9.9 access-control flaw in NetWeaver Visual Composer (CVE-2026-89110), plus 9.9 S/4HANA and 9.1 MII criticals.
SAP's 13 October 2026 Security Patch Day fixes a critical broken-access-control flaw in NetWeaver Visual Composer, CVE-2026-89110 (CVSS 9.9, SAP Note 3797111). It affects VC70RUNTIME 7.50 on the NetWeaver Java stack. Visual Composer was the entry point for the 2025 attacks, so this flaw should go first in the patch queue. No source we read reports exploitation, and the CVE is not in CISA's Known Exploited Vulnerabilities catalog.
SAP's page lists 22 entries: 16 new notes, 4 GitHub advisories and 2 updates. Four of them are rated Critical. The top one, the 10.0 in the Cloud SDK for Python, is covered in our earlier article.
The three criticals and the notes that fix them
| CVE | Product | CVSS | SAP Note | Condition |
|---|---|---|---|---|
| CVE-2026-89110 | NetWeaver Visual Composer, VC70RUNTIME 7.50 | 9.9 | 3797111 | Low privileges |
| CVE-2026-89107 | S/4HANA, Manage Substitution/Validation Rules, S4CORE 105-109 | 9.9 | 3805589 | Low privileges, business authorisation |
| CVE-2026-89108 | Manufacturing Integration and Intelligence, XMII 15.4 and 15.5 | 9.1 | 3798788 | MII administrator |
The note numbers match between SAP's page and the NVD references. Both CVSS 9.9 scores carry a changed scope (S:C), so the damage can reach beyond the vulnerable component.
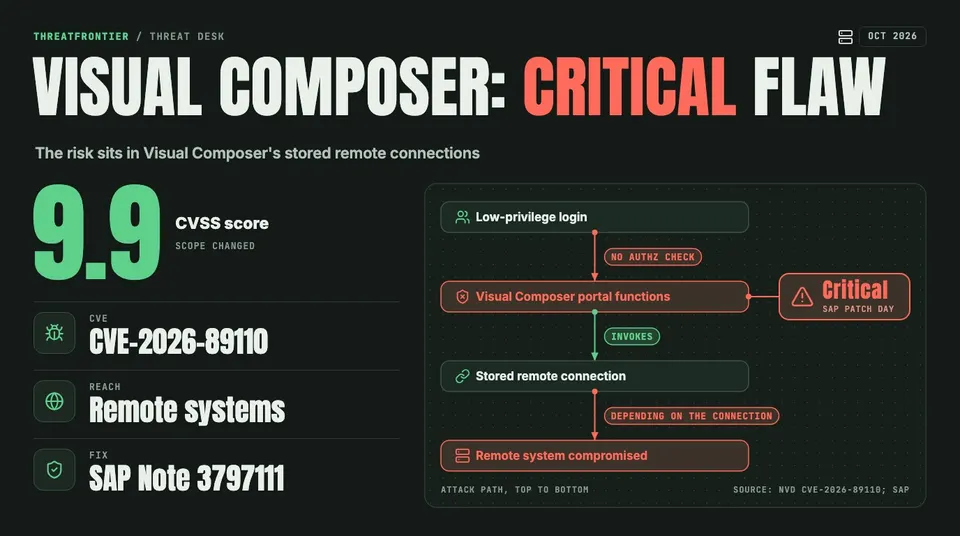
The risk depends on the remote connections Visual Composer holds.
Visual Composer: CVE-2026-89110
Per the CVE record, Visual Composer "does not perform sufficient authorization checks in certain portal functionality." An attacker with low privileges can invoke internal operations on a preconfigured remote system. Depending on how that connection is configured, the result can be full compromise of the remote system. The weakness is CWE-749. The vector is network-reachable, low complexity, no user interaction.
This differs from 2025. The 2025 chain started with an unauthenticated upload. This flaw needs a login, so the exposure depends on who can reach Visual Composer and what back-end systems it is connected to. The risk sits in the remote connections: the more privileged the stored connection, the worse the outcome.
S/4HANA: CVE-2026-89107
Manage Substitution/Validation Rules uses a domain-specific scripting language for rule definitions. Crafted input is interpreted as executable ABAP code by the rule-processing logic. An authenticated user with specific business privileges could run arbitrary ABAP and fully compromise the system. Affected releases are S4CORE 105 to 109 (CWE-94). Systems where many users can edit rules are the priority.
Manufacturing Integration and Intelligence: CVE-2026-89108
A missing authorization check (CWE-862) in the Configuration Service lets an MII administrator provision an account with elevated privileges on the underlying Java application server, extending control past the application. The 9.1 score reflects the high-privilege requirement (PR:H). XMII 15.4 and 15.5 are affected.
Also fixed
- CVE-2026-89113, Commerce Cloud SQL injection (CVSS 8.8, Note 3800517): an authenticated user can read, modify or delete database content. Affects
COM_CLOUD 2211-JDK21. - CVE-2026-58249, memory corruption in the Internet Communication Manager of NetWeaver and Web Dispatcher (CVSS 7.5, Note 3765424): an unauthenticated request can crash the process. Availability only, but it affects many kernel versions, including 7.53, 7.54, 7.77, 7.93 and 9.16.
What to do
- Apply Note 3797111 first on any NetWeaver Java system with Visual Composer installed. Check whether it is deployed at all; if it is not needed, remove it.
- Review the remote connections Visual Composer holds and cut their privileges to what is needed.
- Apply Note 3805589 on S/4HANA, starting where many users hold rule-maintenance rights.
- Apply Note 3798788 on MII and review who holds MII administrator.
- Schedule Notes 3800517 and 3765424. Web Dispatcher and ICM sit at the network edge, so the crash bug matters for availability.
- Keep the 2025 hunting in place: look for unexpected
.jsp,.javaand.classfiles under/irj/directories. The notes themselves need an SAP login.
NVD listed all five records as "Awaiting Analysis" on 18 October, with scores supplied by SAP as the CNA.