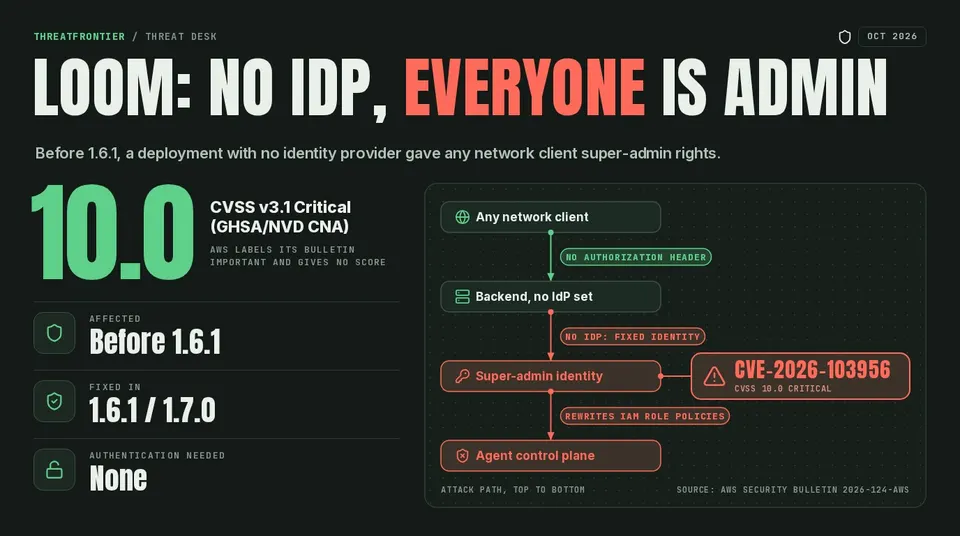
AWS fixes Loom flaw that gave any network client admin rights on deployments without an identity provider
AWS Loom before 1.6.1 treated every client as super-admin with no identity provider set (CVE-2026-103956). Upgrade to 1.7.4; 1.7.0 fixes two SSRF flaws.
· 6 min