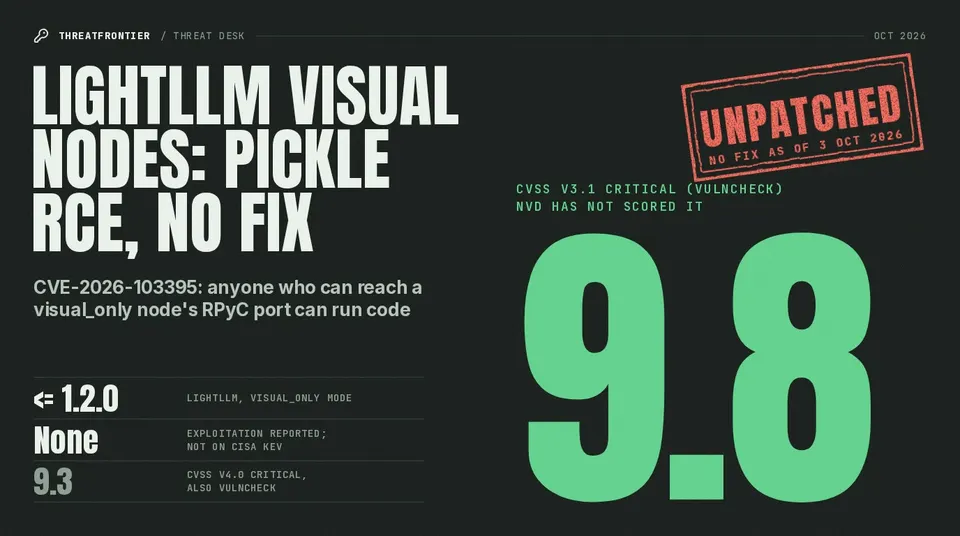
LightLLM Visual Nodes Expose Unauthenticated Pickle RCE (CVE-2026-103395), With No Fix Yet
LightLLM through 1.2.0 runs an unauthenticated, pickle-enabled RPyC service on visual_only nodes. Anyone who can reach the port can run code, and no fix exists yet.
· 6 min