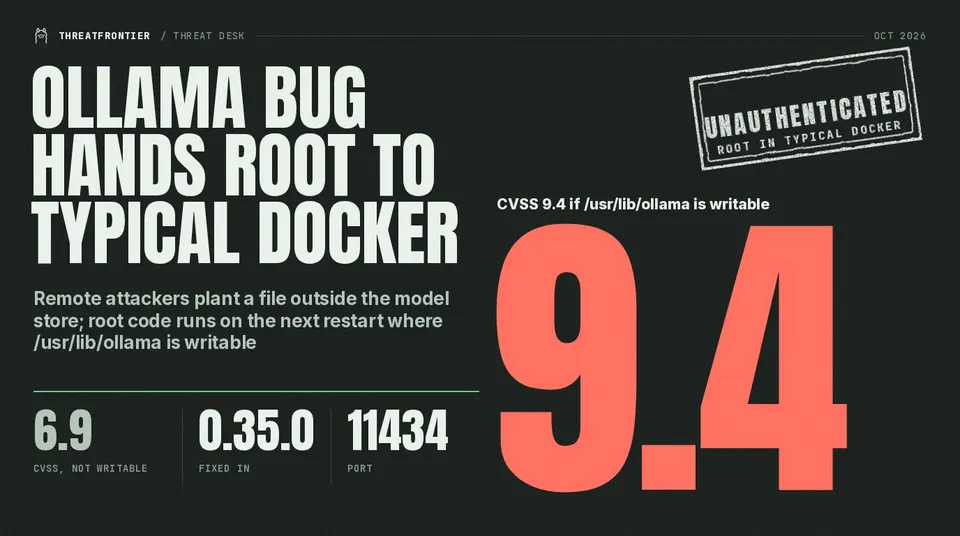
Ollama Path Traversal Lets Remote Attackers Plant Files, and Reach Root in Docker Deployments (CVE-2026-103663)
Ollama's unauthenticated /api/pull path traversal (CVE-2026-103663) can plant a binary that runs as root on restart in Docker. Fixed in 0.35.0.
· 5 min