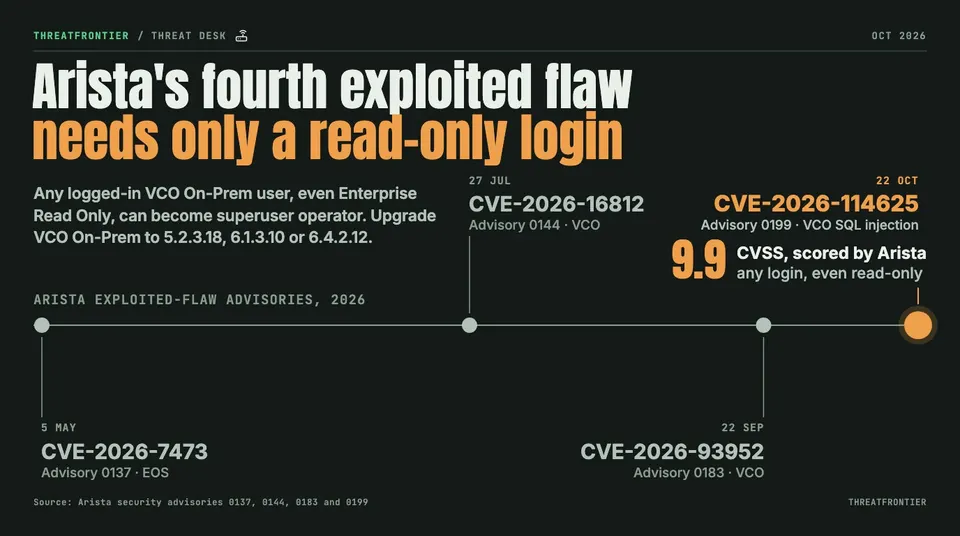
Arista VeloCloud Orchestrator SQL Injection CVE-2026-114625 Is Under Active Attack, and Any Read-Only Login Is Enough
Arista says CVE-2026-114625, a CVSS 9.9 SQL injection in VeloCloud Orchestrator On-Prem, is exploited. Any login, even read-only, reaches superuser.
· 5 min