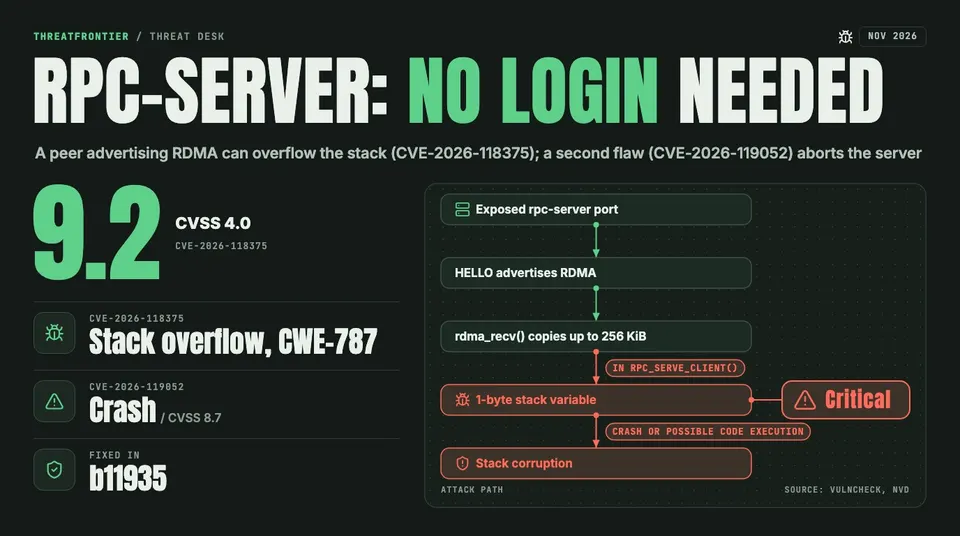
llama.cpp rpc-server Has Two Unauthenticated Flaws: A Stack Overflow Over RDMA and a One-Packet Crash
CVE-2026-118375 lets a peer advertising RDMA write 256 KiB into a 1-byte stack variable; CVE-2026-119052 aborts the server. Update every node to b11935 and keep the RPC port off open networks.
· 4 min