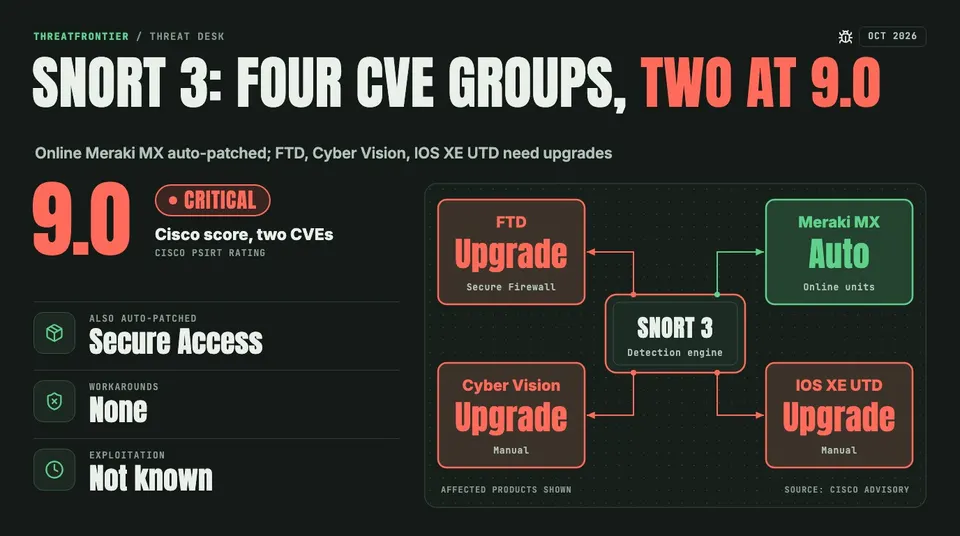
Cisco patched four Snort 3 CVE groups, two scored 9.0. Cloud and online Meraki MX are fixed; FTD, Cyber Vision and IOS XE UTD need upgrades.
Cisco published a Critical advisory on 21 October for four CVE ids in Snort 3, the inspection engine inside several of its security products. Cloud-delivered services and online Meraki MX appliances were patched automatically. Secure Firewall Threat Defense (FTD), Cyber Vision and Unified Threat Defense (UTD) on IOS XE need a manual upgrade, and Cisco lists no workarounds. Cisco says it is not aware of active exploitation.
What is affected
Advisory cisco-sa-hardening-snort3-ybgmhTQe lists Cloud-delivered Firewall, Cyber Vision, Meraki MX, Secure Access, Secure FTD, open-source Snort 3 and UTD on IOS XE. Cisco says they are affected regardless of configuration. Open-source Snort 2 is not affected.
The four CVEs
Each id covers a group of bugs of one weakness class, and its score reflects the most severe bug in the group.
| CVE | Class | Cisco score |
|---|---|---|
| CVE-2026-20043 | Out-of-bounds write (CWE-787) | 9.0 |
| CVE-2026-20236 | Incorrect calculation (CWE-682) | 9.0 |
| CVE-2026-20291 | Improper privilege management (CWE-269) | 7.8 |
| CVE-2026-20356 | Uncontrolled resource consumption (CWE-400) | 7.5 |
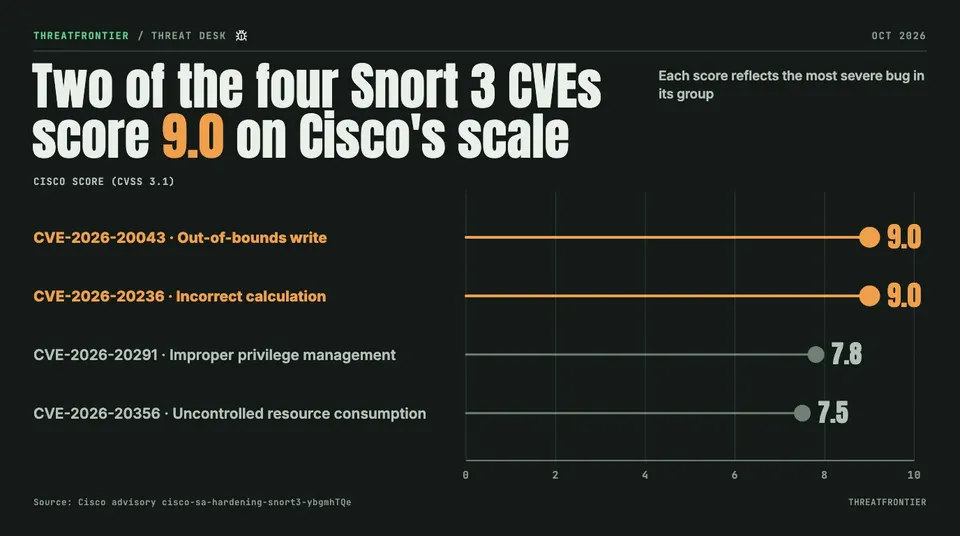
Cisco's advisory scores for the four Snort 3 CVE groups; each score reflects the worst bug in its group.
Cisco found the bugs in internal testing, which it says used its existing processes and frontier AI models. It took the same approach in its October NX-OS hardening release. The advisory was revised on 22 October to correct the UTD fixed-release table, so check the current version before you plan upgrades.
One score differs between sources. The advisory scores CVE-2026-20236 at 9.0, while Cisco's CVE record, as shown on OpenCVE, lists 7.5 with an availability-only vector (AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:H). Cisco does not explain the difference. This article uses the advisory's 9.0.
Patched for you
Cloud-delivered Firewall and Secure Access instances were updated as of 21 October. Meraki MX models that are online and connected to the Meraki Dashboard were updated the same day, with no customer action needed. The advisory's statement covers only online MX units, so bring offline ones back online.
Fixed releases
Everything below needs a manual upgrade. Pick the fixed release in your train.
| Product | Fixed release |
|---|---|
| Secure Firewall Threat Defense | 7.0.10, 7.2.12, 7.4.8, 7.6.6, 7.7.13, 10.0.2, 10.1.0 |
| UTD on IOS XE (images with Snort 3 3.12.4.0) | 17.12.8, 17.15.6, 17.18.5, 26.1.2, 26.2.1 |
| Cyber Vision | 5.6.0 (earlier releases must migrate) |
| Open-source Snort 3 | 3.12.4.0 |
What defenders should do
- Inventory FTD, Cyber Vision, IOS XE UTD and self-built Snort 3 deployments, and upgrade each to the fixed release in its train.
- Confirm Meraki MX units are online and checking in to the Dashboard.
- Start with internet-facing inspection points: the advisory's highest-scored vector is network-reachable without authentication.
- Re-read the advisory for later revisions.