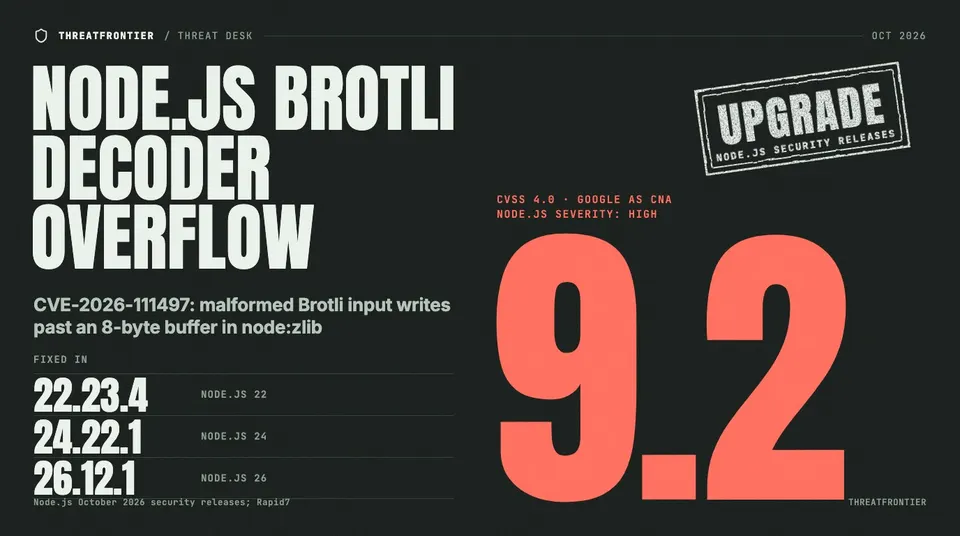
Malformed Brotli input can overflow an 8-byte buffer in Node.js's node:zlib decoder. Node.js 22.23.4, 24.22.1 and 26.12.1 fix CVE-2026-111497.
Node.js released security updates on 21 October 2026 for a memory-corruption flaw in its bundled Brotli decoder, tracked as CVE-2026-111497. It affects the 22.x, 24.x and 26.x release lines, and the fixed versions are 22.23.4, 24.22.1 and 26.12.1. Node.js rates the flaw High. Rapid7 reports that Google, acting as CNA, scores it 9.2 (Critical) under CVSS 4.0. Wiz has named the bug Broccoli2Shell.
Who is affected
An application is exposed when it runs an unpatched 22.x, 24.x or 26.x release and decompresses untrusted Brotli data with node:zlib. Node.js says exploitation can cause a crash, disclosure of process memory or remote code execution. Rapid7 advises treating end-of-life lines as affected and moving to a supported, fixed release.
As of 26 October, Rapid7 knew of no exploitation in the wild, and the CVE was not in CISA's Known Exploited Vulnerabilities catalog. Wiz reports that Ron Masas of Imperva's Red Team demonstrated exploitability, but it links no public proof of concept.
Technical detail
Malformed Brotli input can make the decoder write past the end of an internal 8-byte buffer. According to the Node.js advisory, an invalid block switch was reported as a temporary need for more input rather than a permanent format error. The streaming decoder therefore kept appending input bytes to the buffer. Rapid7 lists the weaknesses as CWE-787 (out-of-bounds write) and CWE-252 (unchecked return value).
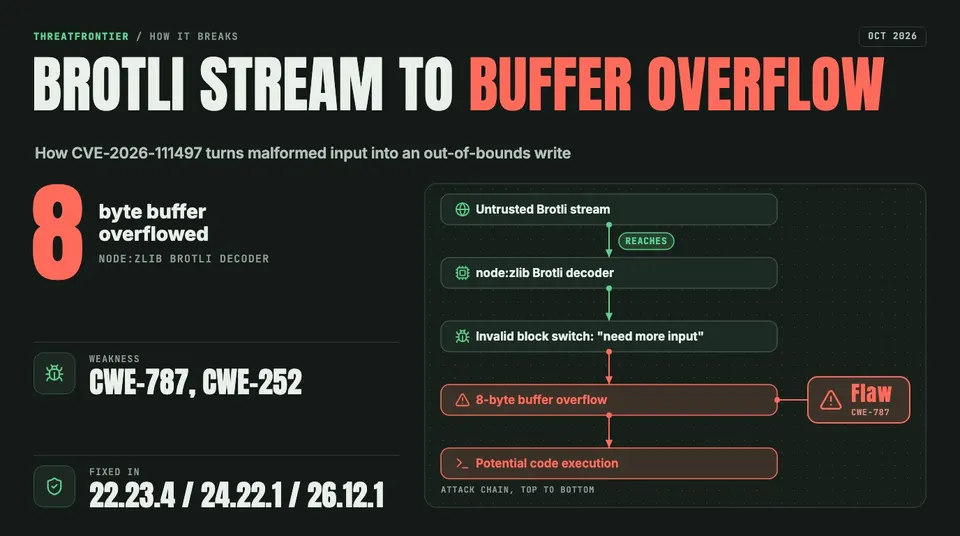
An invalid block switch is treated as a need for more input, so the decoder keeps writing past its 8-byte buffer.
The bug comes from upstream Google Brotli, in versions 1.0.3 before 1.0.10, 1.1.0 before 1.1.1 and 1.2.0 before 1.2.1. OpenAI Codex Security (Khai Tran and Sylvie Mayer) reported it to Node.js, and mcollina and aduh95 fixed it.
The Node.js advisory names node:zlib as the affected interface. Wiz adds that some HTTP clients and frameworks decompress Brotli automatically when that support is enabled, so an application can be exposed without its own code ever calling a Brotli function. Check which of your dependencies decompress Brotli, and where their input comes from.
Beyond Node.js
Because the flaw is upstream, other products ship it too. Wiz lists:
- Bun 1.0.21 to 1.4.3, fixed in 1.4.4
- Python Brotli 1.0.3 to 1.2.0, fixed in 1.2.1, and brotlicffi, fixed in 1.2.1.0
- Envoy, fixed in 1.36.12, 1.37.8, 1.38.6, 1.39.3 and 1.40.0
- Istio, fixed in 1.29.9, 1.30.6 and 1.31.2
- The Go package andybalholm/brotli before v1.2.7
Wiz says its data shows vulnerable resources in 91% of cloud environments and publicly exposed Node.js instances in 82%.
What defenders should do
- Upgrade to 22.23.4, 24.22.1 or 26.12.1, or later. Node.js lists no workaround.
- Rebuild container images, restart processes and confirm that the patched runtime is the one actually running.
- Inventory internet-facing Node.js services first, then gateways and proxies such as Envoy and Istio, then other runtimes and libraries that bundle Brotli.
- If you cannot patch at once, Rapid7 suggests restricting the paths that decompress untrusted Brotli data. Treat that as a stopgap, not a fix.
- Move off end-of-life Node.js lines.