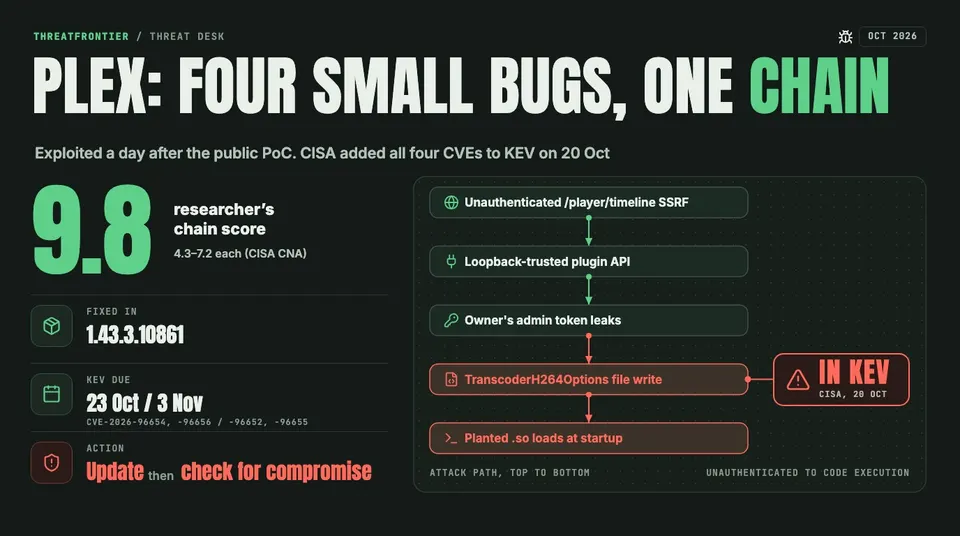
Four Plex Media Server flaws chain into unauthenticated code execution. A public PoC was exploited a day later and CISA added all four to KEV.
CISA added four Plex Media Server vulnerabilities to its Known Exploited Vulnerabilities catalog on 20 October 2026: CVE-2026-96652, CVE-2026-96654, CVE-2026-96655 and CVE-2026-96656. Any server older than 1.43.3.10861 is affected, and Plex says an internet-reachable one should be treated as possibly compromised. Federal agencies must remediate CVE-2026-96654 and CVE-2026-96656 by 23 October; the other two are due 3 November. CISA's entries say each flaw can be chained with the other three.
Why a medium-scored set matters
Taken one by one, the scores are modest. The CISA CNA scored CVE-2026-96652 and -96655 at 4.3 (CVSS 3.1), CVE-2026-96654 at 6.5 and CVE-2026-96656 at 7.2. NVD lists these as "Secondary" scores from CISA's CNA (cisa-cg); it shows no score of its own. The researcher who found the bugs rates the chain at 9.8 Critical, with no authentication needed and code execution as the plex user.
The chain
Zach Main's plex2shell write-up describes five steps:
- An unauthenticated SSRF in
/player/timeline(CVE-2026-96652). The endpoint only checks that an X-Plex-Token header exists, not that it is valid, so the server can be made to call its own loopback interface. - The plugin management API trusts loopback requests, which lets crafted requests reach other plugins' functions (CVE-2026-96654).
- A plugin's URL-fetch function attaches the owner's admin token to any URL starting with
http://127.0.0.1. A hostname with that prefix that resolves to an attacker's IP receives the token. - As admin, the attacker sets the TranscoderH264Options preference, which is appended unsanitized to x264's options, and triggers a transcode that writes attacker-controlled bytes into the codec directory (CVE-2026-96656).
- Plex loads every .so file there at startup without signature, execute-bit or symbol checks, so the planted file runs.
Descriptions differ by source. The CVE record describes CVE-2026-96655 as an authenticated SSRF via /video/:/transcode/universal, while Plex's update describes it as disclosure of the owner's admin token. Read the numbered steps above as the researcher's account, not a one-to-one map of CVE ids.
Exploitation in the wild
The write-up and proof of concept went public on 16 October. A honeypot operator reported the first exploitation on 17 October: requests to /player/timeline/subscribe with a crafted protocol parameter and callback hostnames of the form 127.0.0.1.<attacker-ip>.sslip.io. After outbound traffic was allowed, the honeypot downloaded a cryptominer (xmrig) and a proxy tool called "myawesomeproxy", and saw traffic to proxystream.st. The operator names exploiting IPs 91.92.40.202, 176.65.139.228 and 45.194.92.222. This is one operator's partial data. KEV lists ransomware use as unknown.
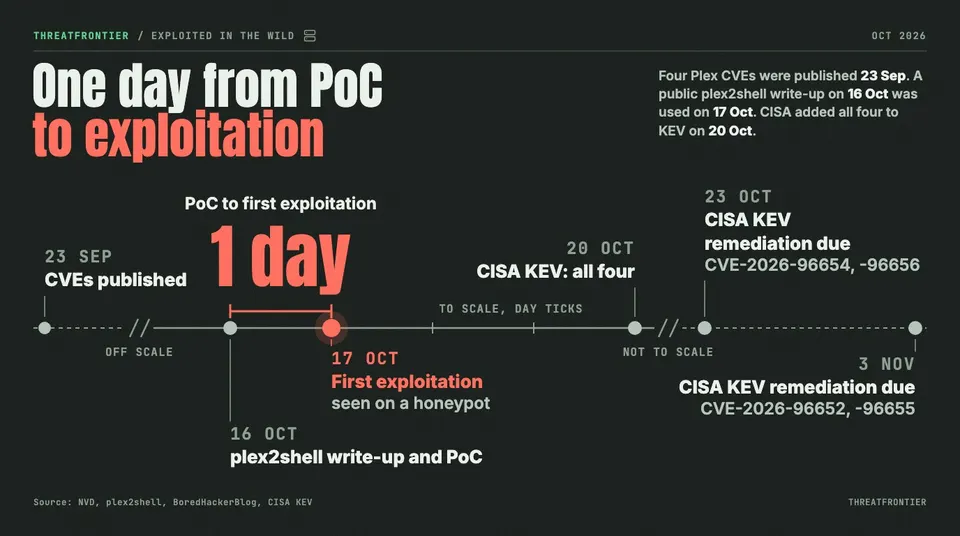
From public proof of concept to first exploitation took one day.
From public proof of concept to first exploitation took one day.
The fixed-version conflict
The fixed build is 1.43.3.10861. Plex's advisory, the CVE record, the NVD description and CISA's CSAF all say so. NVD's CPE data says "versionEndExcluding 1.43.0.10861", which looks like a typo. We found no source that supports it. Match against 1.43.3.10861.
What to do
- Update to 1.43.3.10861 or newer. Plex Desktop 1.115.0 also carries fixes. Verify under Settings, General in Plex Web.
- Turn off Remote Access if you do not need it, and do not forward port 32400 directly.
- Hunt for compromise: unknown child processes of Plex, unfamiliar .so or .dll files in the Codecs folder, odd transcoder options in Preferences.xml, connections to proxystream.st, and high CPU while idle.
- If you cannot rule out compromise, rebuild from a clean install, sign out all devices, change the account password, and treat anything the Plex service account could reach as exposed.
Sources
- NVD CVE-2026-96656: https://nvd.nist.gov/vuln/detail/CVE-2026-96656
- CISA KEV feed: https://www.cisa.gov/sites/default/files/feeds/known_exploited_vulnerabilities.json
- CISA CSAF VA-26-266-01: https://raw.githubusercontent.com/cisagov/CSAF/develop/csaf_files/IT/white/2026/va-26-266-01.json
- CVE record: https://www.cve.org/CVERecord?id=CVE-2026-96656
- Plex advisory: https://forums.plex.tv/t/important-security-update-for-plex-media-server-v1-43-2-and-earlier/942319
- Zach Main, plex2shell: https://zmain.info/blog/plex2shell
- BoredHackerBlog honeypot post: https://www.boredhackerblog.info/2026/10/plex-vulnerabilities-being-exploited-in.html