Oracle's October 2026 patch update fixes 1,295 flaws. Five unauthenticated CVSS 10.0s in SOA Suite, Access Manager and EBS set the first-week order.
Oracle's October 2026 Critical Patch Update, released on 20 October, ships 1,295 new security patches. Within them, the Oracle risk matrices rate five flaws at the maximum CVSS 3.1 score of 10.0. All are reachable over the network without authentication. The affected products are SOA Suite, Access Manager and the Workflow Notification Mailer in E-Business Suite (EBS). WebLogic Server and APEX each carry unauthenticated 9.8 flaws. Oracle's advisory does not say any of these CVEs is being exploited, and this article does not claim they are.
What is in the 10.0 tier
| CVE | Product and component | Protocol | Affected versions |
|---|---|---|---|
| CVE-2026-91216 | SOA Suite, Fabric Layer | T3, IIOP | 12.2.1.4.0, 14.1.2.0.0 |
| CVE-2026-91221 | SOA Suite, Fabric Layer | T3, IIOP | 12.2.1.4.0, 14.1.2.0.0 |
| CVE-2026-91231 | SOA Suite, Adapters | HTTP | 12.2.1.4.0, 14.1.2.0.0 |
| CVE-2026-87337 | Access Manager, Authentication Engine | HTTP | 12.2.1.4.0, 14.1.2.1.0 |
| CVE-2026-101809 | Workflow Notification Mailer (EBS) | HTTP | 12.2.3-12.2.15 |
Every one of them is scored network-reachable, low complexity, no privileges, no user interaction, with scope changed, so a compromise can reach beyond the vulnerable component. The SOA Suite and EBS entries score high impact on confidentiality, integrity and availability. CVE-2026-87337 scores high on confidentiality and integrity and none on availability. Oracle's matrices give no further exploit detail.
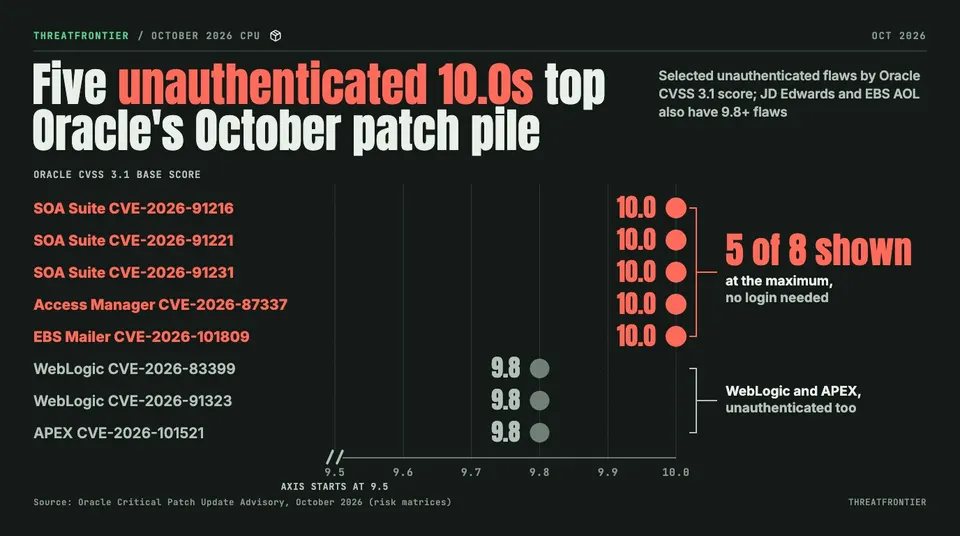
The top of the October CPU by Oracle's own CVSS 3.1 scores; all are unauthenticated.
The top of the October CPU by Oracle's own CVSS 3.1 scores; all are unauthenticated.
The 9.8 tier
- WebLogic Server, Core: CVE-2026-83399 over T3/IIOP and CVE-2026-91323 over HTTP, both unauthenticated, in 12.2.1.4.0, 14.1.1.0.0, 14.1.2.0.0 and 15.1.1.0.0.
- APEX: CVE-2026-101521 over HTTPS, unauthenticated, in 24.1.0-24.1.21, 24.2.0-24.2.20 and 26.1.0-26.1.4. Oracle says both APEX patches in this CPU are remotely exploitable without authentication.
- EBS Application Object Library: CVE-2026-101767, unauthenticated over HTTP in 12.2.3-12.2.15. Oracle credits Brandon Peterson of Horizon3.ai for it.
The matrices also list a sixth 10.0, CVE-2026-91299, in JD Edwards EnterpriseOne Orchestrator (9.2.0.0-9.2.26.5, HTTP). JD Edwards shops should add it to their list.
Scale
Fusion Middleware accounts for 206 of the patches, 134 of them remotely exploitable without authentication. EBS has 194 patches, 31 of them in that category. The volume means triage matters more than completeness in the first week.
What to patch first
This ordering is an editorial judgement from the Oracle scores and exposure, not an Oracle ranking.
- Internet-facing SOA Suite, Access Manager and EBS. These carry the 10.0 scores with scope change. Three of the five are reachable over plain HTTP.
- T3/IIOP exposure. SOA Suite CVE-2026-91216 and -91221 and WebLogic CVE-2026-83399 use T3/IIOP. Check that these ports are not reachable from untrusted networks, whatever the patch state.
- WebLogic 9.8s and APEX. Patch APEX if it is exposed over HTTPS. Confirm your version against the affected ranges above; only 24.1, 24.2 and 26.1 lines are listed.
- Everything else in the CPU, ordered by the remotely exploitable counts above.
Oracle only patches versions under Premier or Extended Support. For older releases it says earlier versions are likely also affected, so plan an upgrade rather than waiting for a fix.
Caveats
Oracle does not publish per-CVE exploitation status, and its boilerplate notes that attackers have attacked customers who had not applied available patches. Read patch details from Oracle's patch availability documents; they were not reviewed for this article.
Sources
- Oracle Critical Patch Update Advisory, October 2026: https://www.oracle.com/security-alerts/cpuoct2026.html