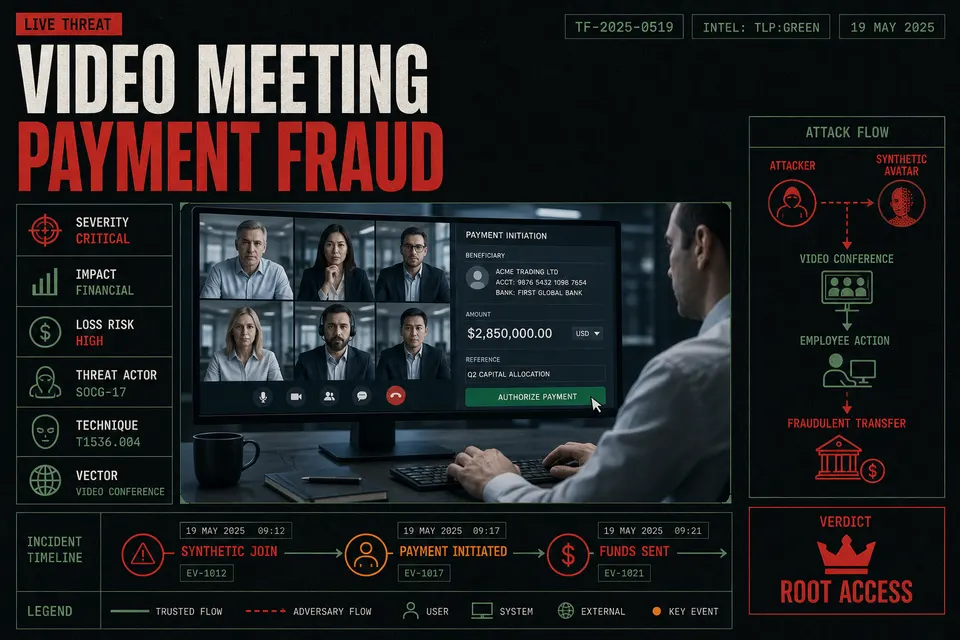
When every participant on the call except the victim is synthetic, conventional MFA and human verification stop being controls. Assurance has to move upstream.
The finance employee joins a video call that looks routine. The chief financial officer is on screen. So are familiar colleagues from legal and operations. Faces match. Voices match. Conversation flows. Near the end, the CFO requests an urgent multi-million-dollar vendor payment. The employee executes the transfers. Only later does the organization learn that nearly every participant except the victim was synthetic.
That pattern—deepfake phishing MFA bypass via real-time voice-video fraud—is operational, not theoretical. Generative AI has made synchronized voice cloning and live synthetic video cheap enough for fraud-as-a-service. Attackers exploit session trust rather than perfect biometrics: camera injection, virtual webcams, live face-swap, and conversational agents now pass video KYC, harvest one-time passwords, and authorize high-value actions. For CISOs and identity architects in banking and large enterprises, the question is how to redesign controls before conventional MFA and human-judged media fully collapse.
How Attackers Fuse Real-Time Voice Cloning with Synthetic Video
The attack chain starts with recon. Public LinkedIn profiles, earnings calls, conference recordings, and social video supply enough face imagery and short audio clips to train clones. Seconds of clean speech can produce a usable voice model; a handful of images support real-time face replacement.
Tooling has followed consumer generative models. Real-time face-swap systems claim sub-50-millisecond latency on ordinary laptops. Virtual camera drivers inject pre-recorded or runtime-rendered streams so applications believe they are receiving hardware webcam input. Conversational agents handle Q&A, urgency scripts, and “poor connection” excuses. Fraud-as-a-service offerings have been marketed in the low tens of dollars per month, collapsing the skill barrier. Enterprise deployments face a parallel weakness, where indirect prompt injection puts enterprise AI agents at risk in ways filters alone cannot stop.
Three production vectors dominate bank onboarding and high-risk authentication in 2026:
- Real-time face-swap on a live laptop session. Passive liveness often passes when micro-movements and lighting are mimicked well enough for the frame stream the verifier sees.
- Camera injection via virtual drivers. The identification client receives a coherent video feed, yet no physical sensor ever captured a live face.
- Voice cloning for spoken challenges, OTP readouts, and security questions. Lip-synced to synthetic video, the multimodal package fools automated checks and human reviewers.
On mobile—especially in APAC banking journeys—the path frequently includes device compromise first: root or jailbreak, app cloning, virtualization, then hooks that replace the camera path while the banking app still believes it talks to a legitimate sensor. Runtime integrity therefore matters as much as the face-match model.
Enterprise business-email-compromise has evolved in parallel. Email or calendar invite builds legitimacy; a cloned voice escalates urgency; a live multi-person deepfake meeting delivers the authorization request. The goal is often not credential theft but wire approval, MFA re-enrollment, or help-desk override. That marks a shift from the pattern still dominating most ransomware intrusions, where compromised credentials overtake vulnerabilities as the primary entry point.
Why Standard MFA Collapses Against Multi-Channel Synthetic Media
Conventional MFA still treats possession of a phone, a push approval, a familiar face, or a coherent voice as proof of presence. Real-time deepfakes turn those factors into social channels.
| Control | Intended trust | Failure under real-time deepfake |
|---|---|---|
| SMS OTP | Possession of phone | Victim reads the code to the “banker” or “CFO” on the deepfake call; adversary-in-the-middle hybrids can intercept live sessions |
| App push / “approve login” | User intent | Urgency plus a familiar face and voice drives approval; no cryptographic origin binding to the legitimate relying party |
| Voice biometrics / “call us back” | Speaker identity | Cloned voice from seconds of public audio; the secondary channel may already be attacker-controlled |
| Video KYC / selfie + liveness | Live presence + match to ID | Injection bypasses the physical sensor; face-swap plus a stolen or synthetic ID passes many pipelines |
| Video call with human | Visual recognition | Real-time synthetic faces and voices; join-time checks miss mid-call swaps when the payment request arrives |
| Knowledge questions | Shared secret | Recon plus an LLM agent answers fluently; nothing is cryptographic |
The technical gap is structural. Presentation attack detection under ISO/IEC 30107-3 addresses physical spoofs at the sensor—photos, masks, screen replays. It does not cover digital injection. Passive or active facial liveness alone is incomplete without camera forensics, device integrity, and continuous verification.
Phishing-resistant authenticators change the equation. Hardware-backed FIDO2 / WebAuthn with origin binding will not complete against a fraudulent relying party even if the human is fully convinced by the deepfake. That is the core distinction between media that humans judge and cryptography that machines enforce. Token-based session trust has its own weak point too: Entra ID's 28-hour token theft gap needs the same scrutiny.
Documented Incidents and the Evidence Base
The flagship public case remains the early-2024 Arup incident in Hong Kong. A finance employee joined a video conference with what appeared to be the UK-based CFO and other colleagues. Reporting described nearly all participants except the victim as AI-generated. Approximately HK$200 million (about $25.6 million) was transferred in a series of fraudulent wires publicly reported as roughly 15 transactions to multiple bank accounts. The company stated that internal systems were not compromised; the loss was authorization fraud enabled by synthetic media, not a network breach. It remains the clearest large-scale proof that multi-participant live deepfake meetings can succeed in the wild.
Regulatory signal followed. On 13 November 2024, the U.S. Financial Crimes Enforcement Network issued an alert on fraud schemes involving deepfake media targeting financial institutions. FinCEN noted rising suspicious activity reports describing deepfake use, especially fraudulent identity documents to circumvent verification and authentication, and published red-flag indicators for Bank Secrecy Act reporting.
Vendor telemetry—directional rather than official global ledgers—points to order-of-magnitude growth in injection and virtual-camera attacks against remote identity verification between 2024 and 2025. Mobile cases in Indonesia, Vietnam, and Thailand illustrate camera-path compromise amplifying face models. Global deepfake fraud loss estimates vary widely across trackers; organizations should treat any single headline total as a range, not a ledger. Public peer-reviewed success rates for live multi-channel deepfake KYC remain scarce. Stronger evidence is the combination of named large-wire success, regulator SAR growth, vendor injection volume, and laboratory defeats of consumer-grade KYC.
Controls That Work Now
No single model stops the threat. Effective stacks combine camera forensics and mobile runtime integrity with continuous meeting verification—because attackers can join “clean” and introduce the synthetic stream only when the high-risk request is made—and with dual-control process gates that stop social authorization even when media looks real.
Identity architects should treat face and voice as risk signals, not sole authenticators for high-risk actions. Separate “match face to document” from “trust the capture pipeline.” Prefer phishing-resistant, origin-bound authenticators for workforce and high-value customer step-up. For wires, beneficiary changes, MFA re-enrollment, and help-desk resets, require dual control plus non-media cryptographic approval.
Prioritized target-state stack
| Priority | Control | Rationale |
|---|---|---|
| P0 | FIDO2 / hardware-backed passkeys | Survives social engineering of humans by synthetic media |
| P0 | Retire SMS OTP as sole high-risk step-up; ban OTP-in-conversation workflows | Codes are harvestable on live deepfake calls |
| P0 | Dual authorization + callback on pre-registered channels for large payments | Defeats Arup-class authorization |
| P1 | Injection-aware liveness + camera forensics on all remote IDV | Closes the ISO PAD gap |
| P1 | Mobile runtime integrity (RASP) on banking apps | Blocks camera-path compromise |
| P1 | Continuous deepfake detection on finance-critical meetings | Catches mid-call swaps |
| P2 | Multimodal risk engines (face + voice + device + behavior) | Single biometric is insufficient |
| P2 | Help-desk re-enrollment treated as privileged ops with hardware proof | Deepfake vishing against service desks |
EU AI Act Article 50 transparency obligations applying from August 2026 require labeling of AI-generated content. Criminals will not label synthetic streams. Compliance is not detection.
While standards mature, ship these highest-leverage actions in weeks:
- Treasury controls — Mandatory dual control above thresholds; no single-person wire from video instruction; cooling periods; verified vendor bank-detail changes.
- MFA and OTP hygiene — Phishing-resistant authenticators for admins and finance; never instruct anyone to read an OTP to a caller; reverse trust so the user initiates a known-good channel.
- KYC RFP language — Explicit coverage of injection, virtual cameras, real-time face-swap, and adversarial false-accept rates—not “iBeta PAD only.”
- Mobile app policy — Integrity, anti-hook, and virtual-environment detection on eKYC and step-up paths; block rooted or cloned sessions for high-risk actions.
- Meeting and awareness policy — Treat finance video meetings as security events; default that video is not identity; drill live deepfake scenarios and callback-to-known-number discipline.
- Detection ops and tabletops — Map FinCEN-style red flags into case management; run an Arup-class multi-participant deepfake payment exercise and measure process stop points.
Forward Risk
Fraud-as-a-service pricing will continue to fall. Agentic multi-channel sequencing will automate the email-to-voice-to-video ladder. A similar leap already happened in ransomware, where JadePuffer marked the first fully agentic extortion campaign. Detection models face a permanent arms race against new generative architectures. Process controls and phishing-resistant cryptography therefore remain the durable foundation.
Under an SMS-plus-video-trust model, residual risk is assessed as critical for remote high-value authorization; under FIDO2, dual control, and injection-aware IDV it drops to medium (still process-dependent). That framing is an editorial risk model, not a measured actuarial rating.
Deepfake phishing MFA bypass succeeds when systems ask people to decide what is real. The organizations that will stay ahead redesign those moments out of the critical path.