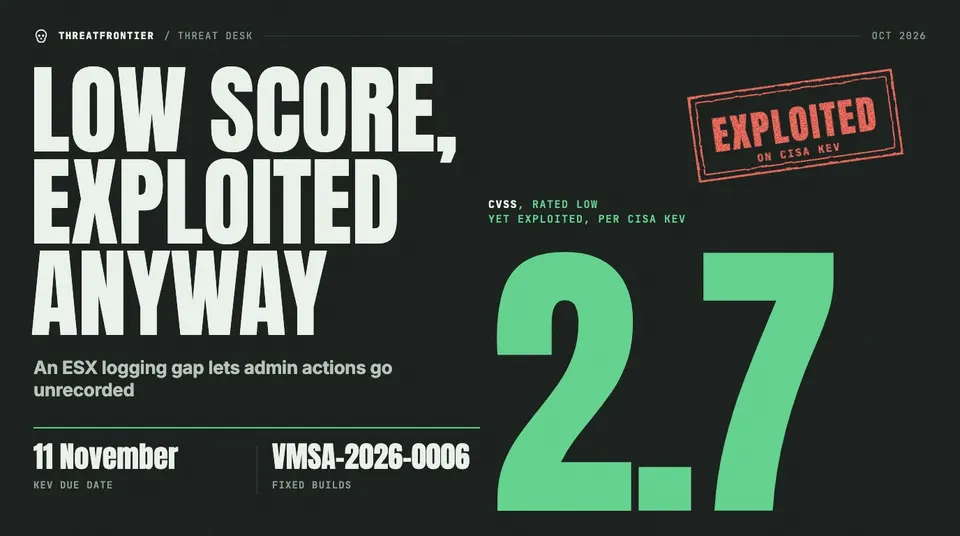
CVE-2026-41709 scores only 2.7, yet CISA lists it as exploited: it lets an ESX admin act without leaving logs. Fixed builds, due 11 November.
CISA added CVE-2026-41709, an insufficient-logging flaw in Broadcom's VMware ESX, to its Known Exploited Vulnerabilities catalogue on 28 October 2026. Federal civilian agencies must remediate by 11 November. The entry confirms active exploitation, but no source we read says who is exploiting it or how.
What the flaw is
Broadcom describes the bug as one where a malicious administrator could perform certain operations on ESX without them being logged. CISA's entry words it the same way and classifies it as CWE-778, insufficient logging. It scores 2.7 (Low); the vector reported by OpenCVE is CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:N/I:L/A:N, so it needs high privileges and gives an attacker no direct access to data or availability.
That score understates the operational risk. The flaw is an anti-forensics aid: an attacker who already holds ESX admin rights can act on a hypervisor host with a gap in the audit trail. Why CISA lists it as exploited is not explained in any source we read. CISA lists known ransomware campaign use as "Unknown".
Advisory and fixed builds
The fix shipped in Broadcom advisory VMSA-2026-0006 (notification 38017), published 29 July 2026 and revised on 3 and 19 August. The advisory does not report exploitation and lists no workarounds. Fixed builds for this CVE:
- ESX 9.1.x: ESXi-9.1.0.0-25370933
- ESX 9.0.x: ESXi-9.0.2.0100-25595025
- ESX 8.0 U3: ESXi80U3j-25429389
- VMware Cloud Foundation 5.x: 5.2.4
- Telco Cloud Platform 5.0.x and 5.1.x: KB449886
The advisory lists no fix for ESX 8.0 U2 or 7.0 against this CVE. Check Broadcom's page for your branch.
The same advisory covers four other flaws, including two 9.8 vCenter issues (CVE-2026-59309, CVE-2026-59310) and a 9.3 ESX VMXNET3 out-of-bounds write (CVE-2026-47876). CISA added CVE-2026-59310 to KEV on 18 August, so this is the second flaw from the advisory on the catalogue. Their fixed builds differ per branch, so check the advisory table.
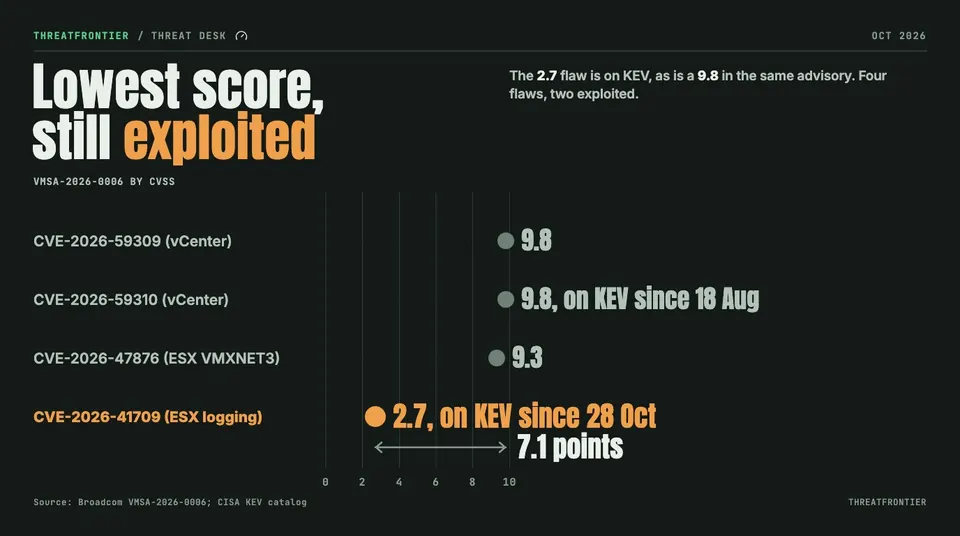
CVE-2026-41709 has the lowest score in VMSA-2026-0006, 2.7 against a top of 9.8, yet it is on CISA KEV, as is CVE-2026-59310.
What defenders should do
- Patch to the fixed builds above; the KEV due date is 11 November.
- Do not treat a clean ESX log as proof of a clean host. Forward ESX logs and vCenter events to an external collector and compare them against other sources such as network flow and identity logs.
- Review who holds ESX administrator rights, and rotate credentials if you suspect an admin account was misused.
- Hunt for administrative activity on hosts that has no matching log entries.
- Patch the critical vCenter and VMXNET3 flaws in the same window.