MemTensor's OpenClaw Plugin and MemoryOS Shipped the sckit Credential Worm
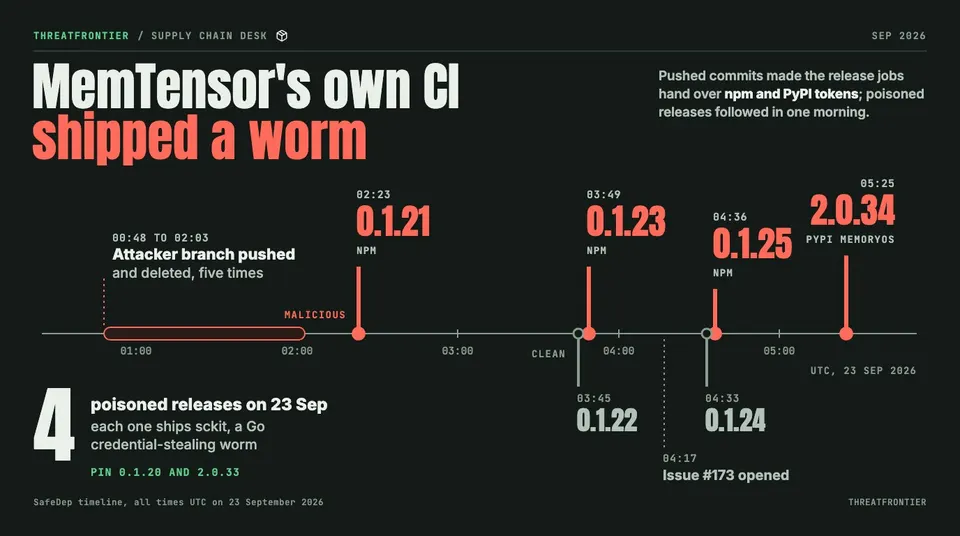
Pushed commits made MemTensor's own GitHub Actions jobs leak npm and PyPI tokens. Four releases then shipped sckit, a Go worm that steals developer secrets.
· 8 minDesk · Software supply chain
Coverage of dependency compromise, build systems, package ecosystems, and vendor risk.
Pushed commits made MemTensor's own GitHub Actions jobs leak npm and PyPI tokens. Four releases then shipped sckit, a Go worm that steals developer secrets.
· 8 min
CVE-2026-33634 turned trusted Trivy releases and GitHub Actions into credential-stealing malware inside CI/CD pipelines and developer environments.
· 5 min
The Mini Shai-Hulud campaign compromised more than 170 reported npm and PyPI packages, exposing how trusted publishing and provenance can still be abused when CI/CD environments are compromised.
· 5 min