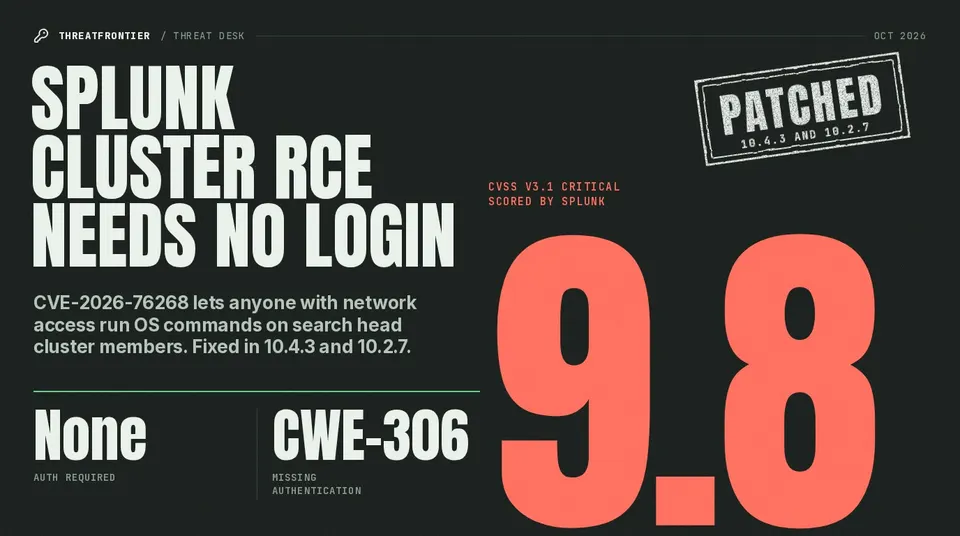
Splunk Enterprise search head clusters exposed to critical unauthenticated RCE in Patroni API (CVE-2026-76268)
Splunk patched CVE-2026-76268, a CVSS 9.8 unauthenticated RCE in the Patroni API on search head cluster members. Fixed in 10.4.3 and 10.2.7; no exploitation stated.
· 5 min