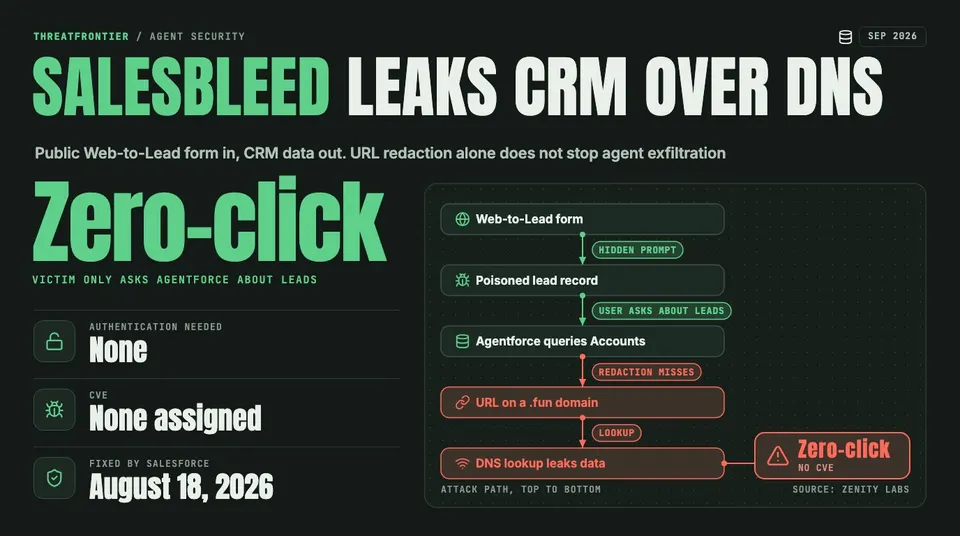
SalesBleed: A Public Web Form Let Attackers Pull Agentforce CRM Data Out Over DNS
Zenity's SalesBleed used a public Web-to-Lead form and two URL-redaction bypasses to make Salesforce Agentforce leak CRM data over DNS.
· 3 minTopic
Coverage tagged prompt injection.
Zenity's SalesBleed used a public Web-to-Lead form and two URL-redaction bypasses to make Salesforce Agentforce leak CRM data over DNS.
· 3 min
Assume injection succeeds, then contain it with architecture, least privilege, isolation and monitoring rather than betting the estate on a single classifier.
· 8 min