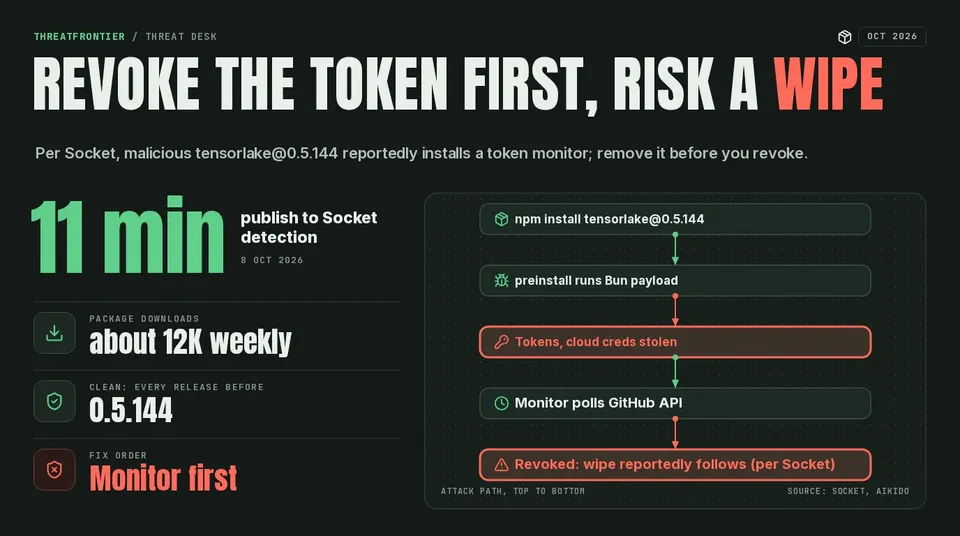
Tensorlake npm Worm: Revoking the Stolen GitHub Token Can Trigger a Home-Directory Wipe, Socket Says
Socket says the malicious tensorlake@0.5.144 npm release plants a token monitor that wipes the home directory if you revoke the stolen GitHub token first.
· 5 min
