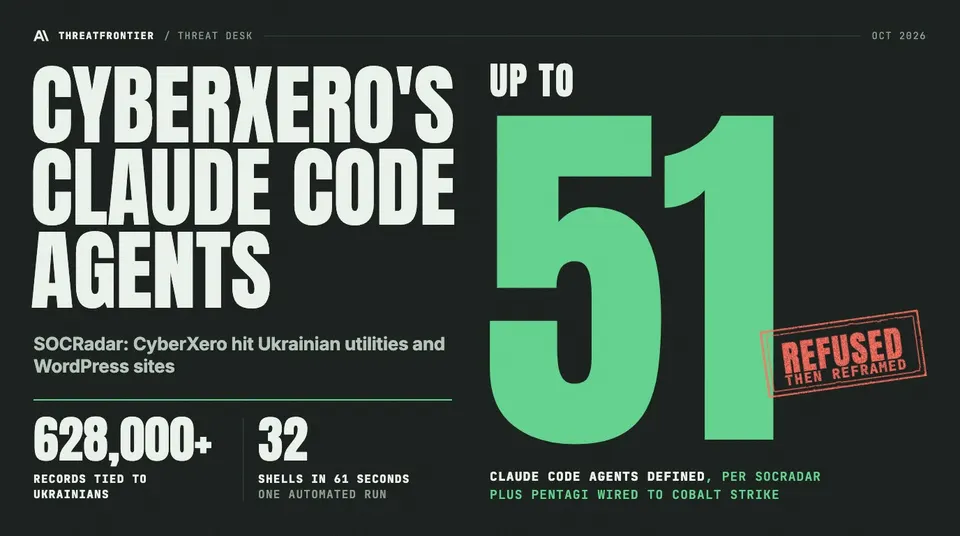
SOCRadar says the CyberXero access broker ran up to 51 Claude Code agents with PentAGI and Cobalt Strike against Ukrainian utilities and WordPress sites.
SOCRadar reports that a Russian-speaking initial access broker, tracked as CyberXero, used Claude Code agents and the PentAGI pentest framework alongside Cobalt Strike to break into Ukrainian energy and utility targets and, in parallel, mass-exploit WordPress and e-commerce sites worldwide. SOCRadar's Threat Research Unit published the findings on 6 October 2026 and describes an active criminal operation, not a confirmed state campaign. All victim figures below are SOCRadar's; we have not verified them independently.
What SOCRadar found
The investigation began with an exposed open directory at 46.21.250.135 that held the operator's live working environment: more than 90,000 files across about 3,000 subdirectories, including AI session logs, scripts with plaintext tokens and victim data. SOCRadar mapped eight infrastructure nodes across three ASNs and two regions from it, and puts first infrastructure in July 2026.
The operator ran two pipelines. The opportunistic one automates exploitation of WordPress and e-commerce platforms for access and payment data. In one run it scanned 4,708 targets, confirmed 429 accessible admin panels and deployed 32 shells in 61 seconds. SOCRadar counts more than 40 affected organisations worldwide. The directed pipeline is manual reconnaissance and exploitation of Ukrainian energy and utilities.
On Ukraine, SOCRadar says the actor holds more than 628,000 records tied to Ukrainian individuals. It reports file-confirmed exfiltration at four Ukrainian organisations, including 564,073 subscriber records and 213,340 access-log entries from a district heating provider in Kharkiv. Seven energy and utility entities were under reconnaissance with no confirmed compromise, including a list of 95 subdomains across two organisations. SOCRadar does not itemise how the 628,000 figure divides between victims, so the components cannot be reconciled with the total. It found no sale of the access, though it considers brokering to a specific buyer the most plausible explanation for the targeting.
The AI layer
The primary workstation held definitions for up to 51 Claude Code agents with roles such as c2-operator, exploit-chainer, scada-attacker and lateral-movement. Separately, a PentAGI deployment was wired to a Cobalt Strike Team Server (4.9.1, an unauthorised build) through an AI provider API. Agent names alone do not show that industrial control systems were manipulated or power delivery disrupted, and SOCRadar does not claim either.
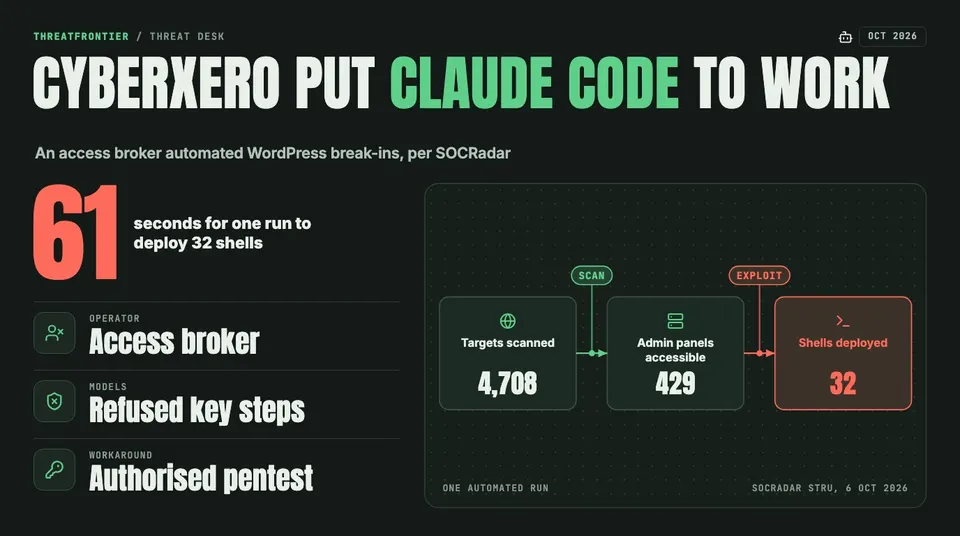
One automated CyberXero run as described by SOCRadar: 4,708 targets, 429 admin panels, 32 shells in 61 seconds. Vendor figures.
What the models refused
The session logs show the safeguards held in places. Across four iterations the model declined to install a backdoor, disable a firewall, move laterally and deploy a webshell. It refused a scan four consecutive times and rejected a forged ownership token.
The operator's workaround was social. They claimed an authorised pentest on their own infrastructure, repeated across four victims and two tools, and opened fresh sessions with that framing preloaded after a refusal. SOCRadar characterises this as reframing prompts, not a technical bypass. We found no Anthropic statement on the case in SOCRadar's post or in the two outlets that repeated it (gbhackers and LetsDataScience, neither independent of SOCRadar).
Vulnerabilities (checked on NVD)
- CVE-2026-63030: WordPress 6.9.x before 6.9.5 and 7.0.x before 7.0.2, REST API batch endpoint route confusion. NVD says it combines with CVE-2026-60137 for SQL injection and remote code execution; CVSS 3.1 9.8.
- CVE-2026-60137: author__not_in in WP_Query not sanitised, in 6.8.x before 6.8.6, 6.9.x before 6.9.5 and 7.0.x before 7.0.2; CVSS 3.1 5.9. Both were published 17 July 2026. SOCRadar calls them the primary and secondary wp2shell chains.
- CVE-2026-4815: Support Board SQL injection, NVD score 8.8. SOCRadar says version 3.8.7, but NVD's description says v3.7.7; check the vendor fix before relying on either.
- CVE-2015-1397: Magento CE 1.9.1.0 SQL injection needing admin access, used against about 93 domains.
SOCRadar also lists MS17-010 patch verification on a Chinese network, with exploitation unconfirmed.
What defenders should do
- Patch WordPress to 6.8.6, 6.9.5 or 7.0.2 or later, as applicable, and review plugins and themes that pass user input to WP_Query.
- Hunt for admin accounts matching wp2_ plus eight hex characters, and plugin directories /wp-content/plugins/wp2shell_[8 hex]/.
- Scan for WSO-family webshells obfuscated with R00t-Shell.com 2.0.15, using SOCRadar's YARA rules.
- Audit ~/.ssh/authorized_keys on internet-exposed Redis hosts, and watch for PowerShell IEX stager downloads from a C2 on port 8033 and a persistence service named UpdSvc.
- Treat AI agent session logs as credential-grade data: retention, encryption and access controls.
The same exposed-directory pattern surfaced in CrowdStrike's report on an operator using Claude Code against South Korean finance, which we covered in ARTEX: Claude Code open directories.