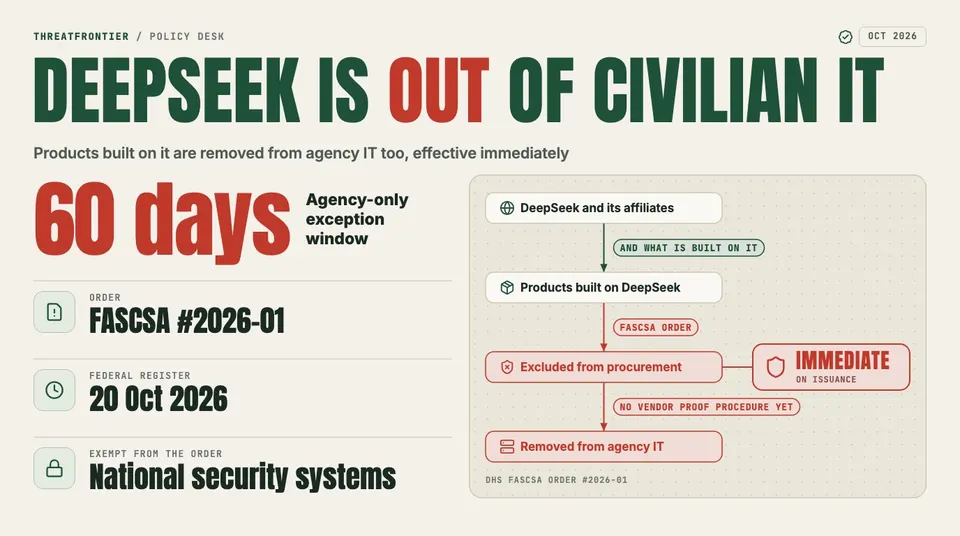
A DHS FASCSA order bars DeepSeek, and third-party products built on DeepSeek models, from federal civilian IT, effective immediately. Vendors should map their models.
The Department of Homeland Security has published a Federal Acquisition Supply Chain Security Act (FASCSA) order that bars DeepSeek from federal civilian procurement and requires agencies to pull DeepSeek products, and third-party products and services built on DeepSeek implementations, out of their IT systems. The notice ran in the Federal Register on 20 October 2026 (Docket DHS-2026-0628, FR Doc 2026-21447). The order itself, Exclusion and Removal Order #2026-01, carries an "Original Release Date" of 24 July 2026.
What the order says
The order is signed by the Secretary of Homeland Security and copied to the OMB Director. It applies to federal civilian executive branch agencies, excluding their national security systems and sensitive compartmented information systems, which fall under Defense and the Director of National Intelligence. Authority is FASCSA (41 U.S.C. 1321-1328) and 41 CFR part 201-1, whose section 201-1.304 requires executive agencies to comply.
It directs two actions, both "effective immediately after issuance":
- Exclude. Agencies must exclude Hangzhou DeepSeek Artificial Intelligence Co., Ltd, its affiliates and their products from procurement. That reaches agency-approved products lists, service provider equipment lists, e-commerce markets and similar functions that enable buying IT hardware, software and services.
- Remove. Agencies must remove products provided by DeepSeek and its affiliates, plus third-party products and services developed using DeepSeek implementations, from civilian agency IT systems, or obtain an exception.
"Affiliate" follows 48 CFR 2.101: one party controls or can control the other, or a third party controls both. A footnote says "DeepSeek implementations" includes third-party implementations used to deliver products and services to civilian agencies. That is the clause that pulls in vendors who wrap, fine-tune or host DeepSeek models.
Stated rationale
DHS describes DeepSeek as a privately owned PRC company whose servers sit in China, where the legal system permits broad government access to private infrastructure. For DeepSeek-hosted instances, account creation collects personally identifiable information and may fingerprint users. Prompts entered by government employees or vendors could carry sensitive data to the PRC. The order also says the models "may contain malware or other security vulnerabilities" and cites open-source research (NowSecure) reporting critical flaws in the DeepSeek iOS app.
Exceptions and timing
Only agencies can ask for exceptions, not vendors. Requests go in writing to the DHS issuing official under 41 CFR 201-1.304(b) within 60 days of issuance, and must name the order, describe the exception or delay sought, identify the covered product, give a compelling justification (mission-critical impact or national-interest considerations) and propose alternative mitigations. CISA approves or disapproves in writing at FASCSA.Orders@cisa.dhs.gov. The order sets no calendar removal deadline: the text says "immediately". Until removal is complete, agencies are encouraged to monitor traffic, add logging and exfiltration controls and flag anomalous activity. The Secretary must review the order within a year and annually after that.
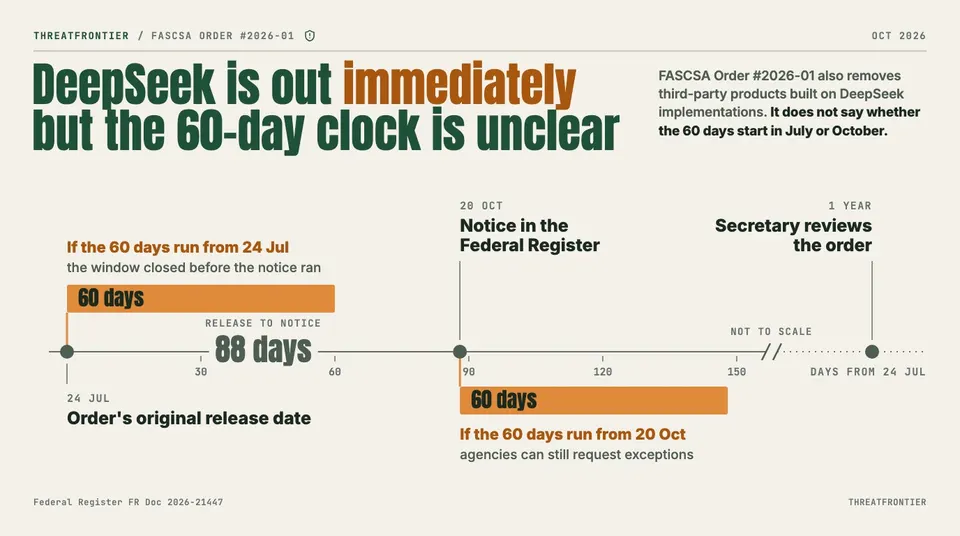
What the order fixes in time, and what it leaves unclear.
What the order fixes in time, and what it leaves unclear.
The order does not say whether the 60 days run from the 24 July release date or from the Federal Register notice. If measured from July, the window would already have closed. The order text does not settle this.
What it does not say
The published order contains no contractor flow-down clause and no vendor certification or AI bill-of-materials procedure. It does not define how a vendor proves its stack is free of DeepSeek models. Vendors should expect agencies to ask, and the practical exposure is the "developed using DeepSeek implementations" language. Any claim about specific representations or contract clauses should wait for CISA, OMB or FAR Council guidance. The regulations.gov docket returned HTTP 403 during research, so the Federal Register copy is the text relied on.
What defenders and vendors should do
- Agencies: inventory SaaS, copilots, chat and coding tools, and embedded model APIs for DeepSeek weights or hosted endpoints; strip them from catalogues and approved lists; decide quickly whether an exception request is needed.
- Vendors selling to civilian agencies: map which models sit behind each feature, including distilled, fine-tuned or self-hosted DeepSeek derivatives and subcontractor components, and be ready to document that mapping.
- Security teams generally: egress monitoring for DeepSeek endpoints and logging on AI tools follows the order's own interim advice.
Sources
- Federal Register notice and order, FR Doc 2026-21447: https://www.govinfo.gov/content/pkg/FR-2026-10-20/pdf/2026-21447.pdf
- Public inspection copy: https://public-inspection.federalregister.gov/2026-21447.pdf