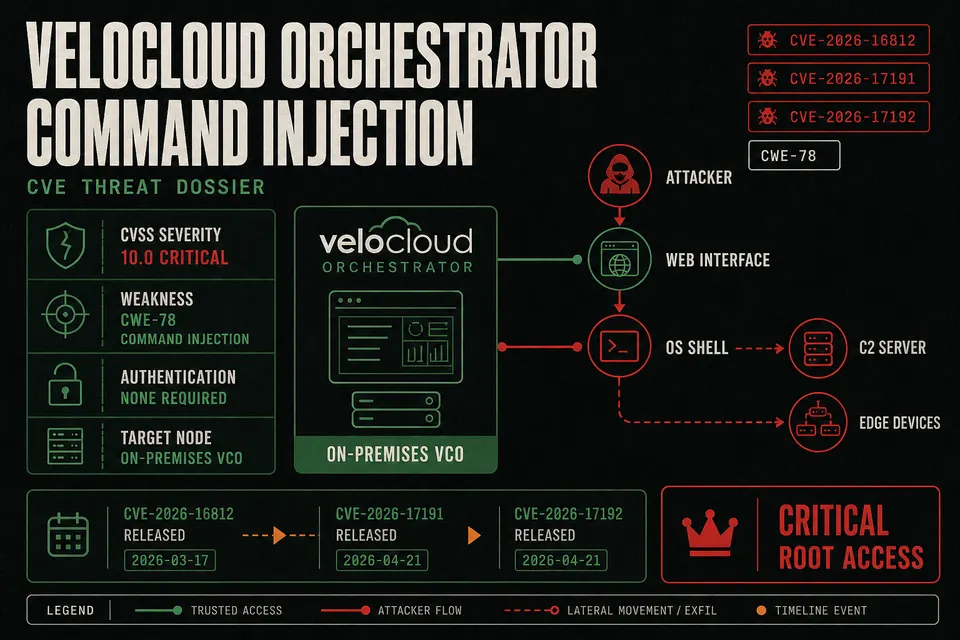
Critical CVSS 10.0 zero-day CVE-2026-16812 hits Arista VeloCloud Orchestrator. Learn how to hunt for active exploits, patch versions, and isolate management…
The discovery of active zero-day exploitation targeting on-premises Arista Networks VeloCloud Orchestrator deployments has shifted enterprise risk from routine vulnerability patching to an urgent threat-hunting imperative. Tracked as CVE-2026-16812, the maximum-severity flaw carries a CVSS 10.0 (Critical) score under both CVSS v3.1 and CVSS v4.0 metrics (AV:N/AC:L/PR:N/UI:N/S:C/C:H/I:H/A:H). The vulnerability stems from an unauthenticated OS command injection weakness (CWE-78) within internal management functions. Because the flaw allows remote, unauthenticated attackers to execute arbitrary system commands with complete administrative privileges over exposed Orchestrator nodes, federal cyber authorities have designated the vulnerability for mandatory emergency remediation. SD-WAN management planes have been a state-actor target before, as in the Versa zero-day used to breach telecom SD-WAN systems.
Update, 2 October 2026: A second actively exploited Orchestrator flaw, CVE-2026-93952 (CVSS v3.1 10.0), was disclosed in Arista Security Advisory 0183 and added to the CISA Known Exploited Vulnerabilities catalog on 22 September 2026. Every release that fixed CVE-2026-16812 is still vulnerable to it. Fixes exist only in 5.2.3.16 and 6.4.2.8 so far. Details and hunting guidance are in the CVE-2026-93952 section below.
Technical Anatomy of CVE-2026-16812 Command Injection
The root mechanism of CVE-2026-16812 resides in a vulnerable internal management endpoint designed exclusively for local system operations. During initial product assembly, this endpoint was bundled into the main web application stack without restricting network accessibility or enforcing session authentication. Consequently, any network path capable of delivering HTTP or HTTPS traffic to the VeloCloud Orchestrator (VCO) web management interface provides an unauthenticated vector for command injection.
Crucially, no native product configuration toggle exists within vulnerable software releases to disable access to this internal endpoint. The flaw affects four major enterprise release trains, while cloud-hosted and dedicated cloud instances were patched prior to public disclosure.
| Software Release Train | Vulnerable Version Range | Remediated Release | Vulnerability Status |
|---|---|---|---|
| VeloCloud Orchestrator 5.2.x | Versions prior to 5.2.3.14 | 5.2.3.14 | Unauthenticated Zero-Day (Exploited) |
| VeloCloud Orchestrator 6.1.x | Versions prior to 6.1.3.4 | 6.1.3.4 | Unauthenticated Zero-Day (Exploited) |
| VeloCloud Orchestrator 6.4.x | Versions prior to 6.4.2.4 | 6.4.2.4 | Unauthenticated Zero-Day (Exploited) |
| VeloCloud Orchestrator 7.0.x | Versions prior to 7.0.0.1 | 7.0.0.1 | Unauthenticated Zero-Day (Exploited) |
Critical Risk Note: Legacy versions of VeloCloud Orchestrator at End-of-Support (EOS) were not evaluated. Organizations running legacy builds must treat those instances as vulnerable and immediately upgrade to supported release trains.
Defenders should also address companion maintenance vulnerabilities resolved in the same patch cycle, including CVE-2026-17191 (CVSS 9.1, SQL injection in the Flow Metrics API) and CVE-2026-17192 (CVSS 8.5, Server-Side Request Forgery). While these secondary flaws require prior authentication, deploying the consolidated update resolves the entire attack surface.
A Second Exploited Flaw: CVE-2026-93952
On 22 September 2026, 57 days after CVE-2026-16812 entered the KEV catalog, Arista published Security Advisory 0183 for CVE-2026-93952. It is a separate improper input validation flaw (CWE-20) in on-premises VeloCloud Orchestrator. Arista says it "may allow a remote attacker to access privileged internal functionality and impact the VCO host," and that the issue "was discovered externally and is known to be actively exploited." CISA added it to the KEV catalog the same day, with a remediation due date of 25 September 2026 for federal agencies and a forensic triage requirement.
- Severity: CVSS v3.1 10.0 (
AV:N/AC:L/PR:N/UI:N/S:C/C:H/I:H/A:H); CVSS v4.0 9.5 (AV:N/AC:H/AT:N/PR:N/UI:N/VC:H/VI:H/VA:H/SC:H/SI:H/SA:H). - Preconditions: The Orchestrator is exposed if certificate-based authentication from VeloCloud Edge to the Orchestrator is configured. The attacker needs the public portion of an Edge authentication certificate and network access to the VCO web interface. Tenant or operator credentials are not required.
- Scope: On-premises Orchestrator only. Arista says hosted and dedicated VCO instances were affected and have already been patched. VeloCloud Edge and Gateway are not affected.
The releases that closed CVE-2026-16812 all fall inside the CVE-2026-93952 affected ranges, so a host patched in July is still exposed:
| Release Train | CVE-2026-16812 Fix | CVE-2026-93952 Affected | CVE-2026-93952 Fix |
|---|---|---|---|
| 5.2.x | 5.2.3.14 | 5.2.3.15 and below | 5.2.3.16 |
| 6.1.x | 6.1.3.4 | 6.1.3.7 and below | No fixed release yet |
| 6.4.x | 6.4.2.4 | 6.4.2.7 and below | 6.4.2.8 |
| 7.0.x | 7.0.0.1 | 7.0.0.2 and below | No fixed release yet |
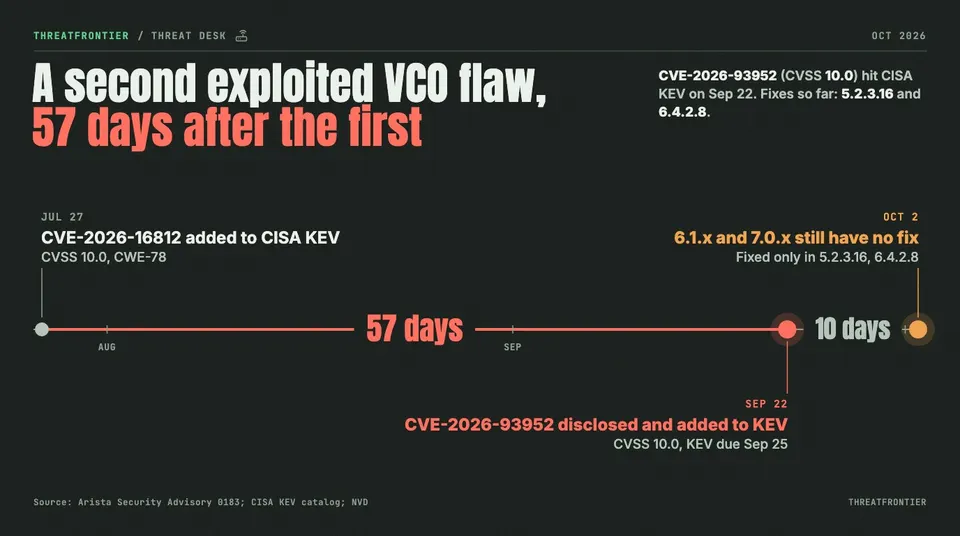
Two actively exploited VeloCloud Orchestrator flaws, 57 days apart. As of 2 October 2026, CVE-2026-93952 is fixed only in 5.2.3.16 and 6.4.2.8. Sources: Arista Security Advisory 0183, CISA KEV, NVD.
As of 2 October 2026 the advisory lists fixes only for the 5.2.3 and 6.4.2 trains and says releases for other trains "will be added over time." Operators on 6.1.x or 7.0.x should move to a fixed train where they can, or contact Arista TAC about upgrade options. Until then, Arista recommends restricting the VCO web interface to trusted administrative networks, blocking outbound ports not needed for normal operation, and monitoring for backdoor daemons and webshells. Arista also warns that a compromised Orchestrator "may allow attackers access to the VeloCloud Edge devices as well," so post-remediation work should include credential rotation and validation of managed device state.
Forensic Playbook: Inspecting Orchestrator Access Logs and System Artifacts
Because public exploitation began prior to patch availability, enterprise security operations centers must conduct retrospective threat hunting across all on-premises Orchestrator nodes. Hunts should allow for more than one intruder, as when rival China- and India-linked actors converged on the same networks. Initial access attempts leave distinct traces across web access logs, API gateway logs, and operating system audit records.
Threat hunters should query web server access logs for command separators, subshell expansions, or URL-encoded payloads inserted into URIs and POST parameters.
# Search Nginx/Apache web access logs for shell injection syntax and known IP IOCs
grep -E '(8\.19\.75\.217|206\.72\.242\.124|206\.72\.242\.162)' /var/log/nginx/access.log

# Scan web logs for command separator characters and system binary references
egrep -i '(%20|%0a|%0d|\|\|\;|\`|\$\().*(wget|curl|python|bash|sh|nc|tftp|certutil)' /var/log/nginx/*access*.log
Incident response teams should cross-correlate four primary data sources to confirm post-exploitation activity:
- VCO Web Access Logs: Examine incoming HTTP verbs, payload lengths, and client IP addresses for requests targeting internal endpoints.
- Backend Application Logs: Identify runtime exceptions, unexpected subprocess invocations, or abnormal API queries originating from local host processes.
- OS Audit Logs (
/var/log/audit/audit.log,/var/log/syslog): Look for process creation events (execve) where web server processes spawn shell interpreters (/bin/sh,/bin/bash). - Database Access Logs: Review queries exporting tenant inventories, API tokens, cryptographic certificates, or site-to-site VPN keying material.
For CVE-2026-93952, Arista says there is no single definitive indicator of compromise. It lists specific files, a request header and two source IP addresses, and asks operators who find them to preserve the VCO's state and contact TAC:
# CVE-2026-93952 indicators from Arista Security Advisory 0183
ls -la /usr/local/sbin/.vcnode.js /usr/local/sbin/vc-sysmond /etc/systemd/system/vc-sysmon.service 2>/dev/null
md5sum /usr/local/sbin/.vcnode.js 2>/dev/null   # known malicious: dc78e206eaeadec59fc5801fe4556bd0
grep -il 'x-vc-opt' /var/log/nginx/*.log
grep -E '(142\.93\.149\.77|104\.248\.126\.159)' /var/log/nginx/*access*.log
Indicators of compromise identified in active threat campaigns against both flaws include the following:
| Indicator Type | Value / Hash / Descriptor | Context & Threat Activity |
|---|---|---|
| IPv4 Address | 8[.]19[.]75[.]217 | Inbound exploit delivery and reconnaissance |
| IPv4 Address | 206[.]72[.]242[.]124 | Primary C2 and payload retrieval server |
| IPv4 Address | 206[.]72[.]242[.]162 | Secondary scanning and command execution host |
| IPv4 Address | 142[.]93[.]149[.]77 | CVE-2026-93952: connections listed by Arista Advisory 0183 |
| IPv4 Address | 104[.]248[.]126[.]159 | CVE-2026-93952: connections listed by Arista Advisory 0183 |
| File | /usr/local/sbin/.vcnode.js (MD5 dc78e206eaeadec59fc5801fe4556bd0) | CVE-2026-93952: known malicious file |
| File | /usr/local/sbin/vc-sysmond, /etc/systemd/system/vc-sysmon.service | CVE-2026-93952: backdoor daemon and its systemd unit |
| HTTP Header | x-vc-opt in nginx logs | CVE-2026-93952: request header Arista lists as an indicator |
| MITRE ATT&CK | T1059.004 (Unix Shell) | Post-exploitation command execution |
| MITRE ATT&CK | T1190 (Exploit Public-Facing Application) | Initial access via unauthenticated endpoint |
Forensic Guidance: Post-exploitation indicators include unauthorized file placement in web directories, scheduled job creation in
/etc/cron.*, and outbound persistent TLS connections from Orchestrator host IPs toward external command-and-control nodes.
Remediation Beyond Patching: Restricting Management Planes and Network Segmentation
Deploying vendor updates eliminates the code vulnerability, but durable defense requires structural isolation of the SD-WAN management plane. Enterprise architectures must enforce strict separation between management controllers, control-plane signaling, and user data-plane transit. Cisco's own SD-WAN controller faced a comparable exposure; see Cisco's critical Catalyst SD-WAN zero-day, CVE-2026-20182.
To secure on-premises Orchestrator instances against future zero-day vectors, network infrastructure teams must implement four core controls:
- Out-of-Band Management Isolation: Move the VCO web interface off general enterprise networks into a dedicated Out-of-Band (OOB) management VLAN accessible only via Zero-Trust Network Access (ZTNA) gateways or jump hosts.
- Strict Inbound Access Control Lists (ACLs): Apply hardware firewall filters restricting inbound TCP ports
80and443strictly to trusted administrative IP ranges. - Egress Traffic Filtering: Restrict outbound host connections to verified update repositories and threat intelligence feeds.
- Interactive Shell Hardening: Enforce multi-factor authentication for SSH sessions and route system administrative commands through privileged access management platforms.
Long-Term Governance for Enterprise SD-WAN Controllers
Maintaining operational continuity while isolating a compromised management plane presents a key operational challenge. Fortunately, VeloCloud SD-WAN architecture decouples the control and management planes from the data plane. For a comparable triage playbook on another edge appliance, see the SonicWall SMA 1000 zero-day attack chain.
When a VeloCloud Orchestrator node is isolated or powered down for forensic investigation, underlying VeloCloud Edge devices continue forwarding data-plane traffic over established overlay tunnels without interruption. This architectural independence allows incident response teams to quarantine a suspect Orchestrator without disrupting branch WAN connectivity.
Security teams should follow an automated incident recovery workflow when responding to potential management plane compromise:
# Incident Response Protocol: SD-WAN Management Plane Quarantine
def execute_orchestrator_isolation(instance_id):
 # Step 1: Capture non-volatile forensic memory and disk snapshots
 capture_forensic_snapshot(instance_id)

 # Step 2: Restrict network interface to forensic collection VLAN
 reassign_network_vlan(instance_id, target_vlan="ISOLATION_FORENSICS_ONLY")

 # Step 3: Verify branch data plane continuity across active Edges
 status = check_edge_data_plane_status()
 if status == "STABLE_FORWARDING":
 # Step 4: Provision clean, parallel Orchestrator instance from trusted media
 # 7.0.0.1 fixed CVE-2026-16812 but not CVE-2026-93952; as of 2 Oct 2026 only 5.2.3.16 and 6.4.2.8 fix both
 deploy_parallel_orchestrator(version="6.4.2.8")
 # Step 5: Rotate root certificates, API tokens, and Edge credentials
 rotate_infrastructure_secrets()
To ensure long-term resilience, organizations must integrate SD-WAN controllers into automated vulnerability scanning routines, enforce configuration drift detection, and execute routine failover drills. Combining rapid patching with zero-trust network isolation ensures single-point software vulnerabilities cannot compromise broader enterprise operations. The same rapid-patch-plus-isolation discipline applies to Oracle WebLogic's critical proxy-bypass flaw under mass exploitation.
Sources
- NVD: CVE-2026-93952
- Arista Security Advisory 0183 (CVE-2026-93952)
- CISA Known Exploited Vulnerabilities catalog: CVE-2026-93952
- NVD: CVE-2026-16812