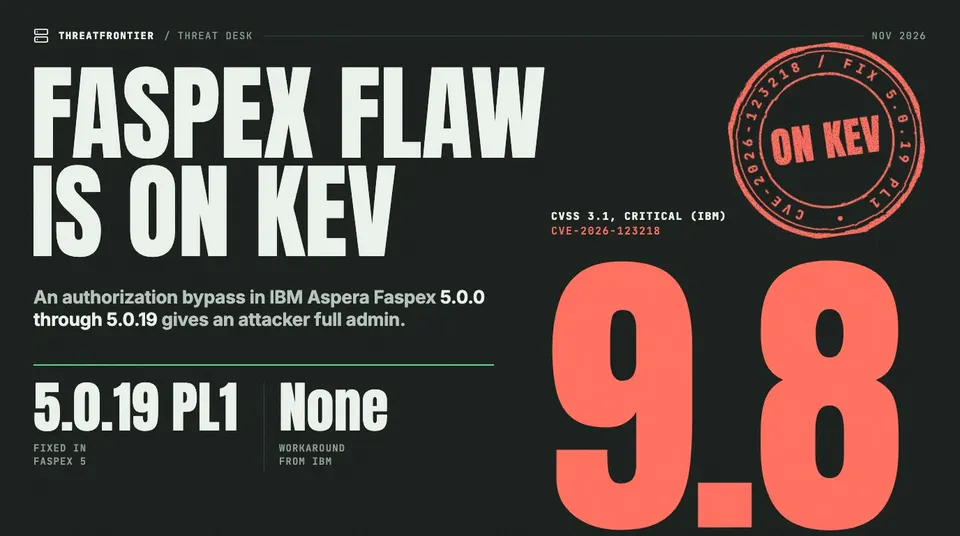
CISA added IBM Aspera Faspex 5 bug CVE-2026-123218 (CVSS 9.8) to KEV two days after IBM's bulletin. It grants full admin; upgrade to 5.0.19 PL1.
CISA added CVE-2026-123218, an authorization flaw in IBM Aspera Faspex 5 that hands an attacker full administrative privileges, to its Known Exploited Vulnerabilities (KEV) catalog on 9 November 2026, two days after IBM published its bulletin on 7 November. Faspex 5.0.0 through 5.0.19 is affected. The fix is 5.0.19 PL1, and IBM lists no workaround.
What the flaw is
IBM's bulletin says an authenticated user could craft a specific message to bypass authorization and gain full administrative privileges. The weakness is classed as CWE-863 (Incorrect Authorization). IBM scores it 9.8 under CVSS 3.1, with the vector CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H.
The score and the description disagree. The vector says no privileges are required (PR:N), while the text says the attacker is an authenticated user. IBM does not reconcile the two, so the access an attacker needs is unclear from the bulletin. IBM credits no one and gives no technical detail beyond that one sentence, and no exploitation details are public.
The KEV listing
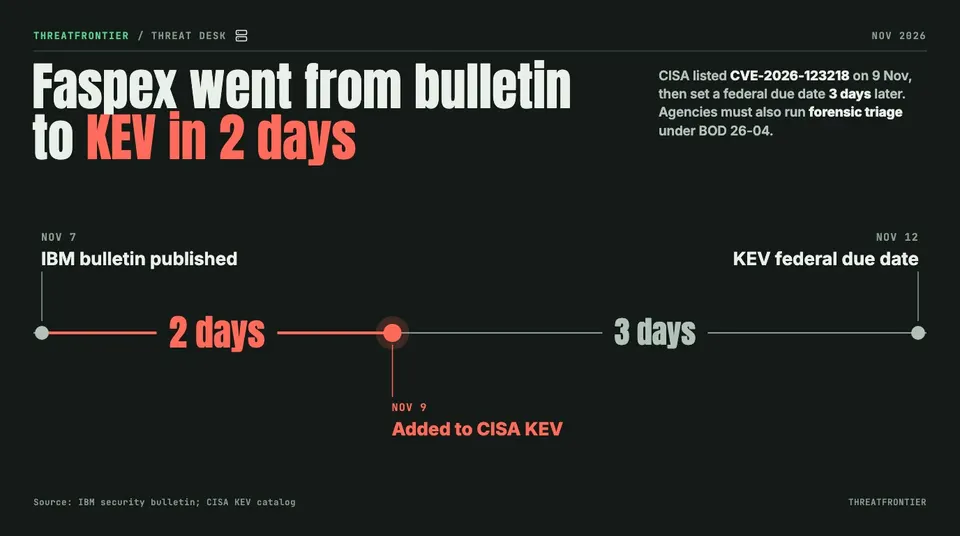
From IBM's bulletin to the KEV listing to the federal due date. Sources: IBM security bulletin, CISA KEV catalog.
The timeline is short: 2 days from IBM's bulletin to the KEV listing, then 3 days to the federal due date of 12 November 2026. The required action is to apply mitigations per vendor instructions and follow BOD 26-04, and the entry marks forensic triage as required under BOD 26-04. Known ransomware use is listed as "Unknown". We found no public detail on who is exploiting the flaw or how widely.
That due date has passed. Federal agencies that have not patched are already late, and everyone else should treat the upgrade the same way.
What to do
- Upgrade to Faspex 5.0.19 PL1 (Linux). IBM strongly recommends it and offers no workaround.
- Verify the build. The faspex-core container image should read 5.0.19 (1ce4b13, Fix Pack: 1).
- Check for misuse. The flaw grants full admin, and CISA asks agencies for forensic triage, so review admin accounts and audit logs for changes nobody on your team made. This is general incident-response practice, not IBM guidance.
KEV-listed authorization bypasses that end in admin access are a recurring pattern; see the WSO2 API Manager JWT bypass and the Cisco ISE zero-day. For hardening the portals that move files between organisations, see our guide to securing third-party data exchange portals.