SAP's November Patch Day fixes four pre-auth CVSS 10.0 bugs in ICM, Web Dispatcher, Gateway and SAML2; Onapsis holds a working ICM2SHELL exploit.
SAP's November 10, 2026 Security Patch Day fixed four vulnerabilities that SAP rates CVSS 10.0, according to The Hacker News and BleepingComputer, and none of them needs a login. Two of them, CVE-2026-76964 and CVE-2026-89126, are one shared bug that Onapsis calls ICM2SHELL: it sits in the code that NetWeaver's Internet Communication Manager (ICM) and the SAP Web Dispatcher use to handle WebSocket traffic, and Onapsis says it gave SAP a working exploit that runs operating-system commands as the <sid>adm account that owns the SAP installation. A third, PROXYGATE (CVE-2026-89103), is in SAP Gateway and needs a configuration change on top of the patch. The fourth, CVE-2026-120017, lets an attacker log in as any user on some SAML single sign-on setups.
If you run SAP NetWeaver AS ABAP, a Web Dispatcher, SAP Gateway or SAML logon on ABAP, treat this as an urgent patch cycle: patch the kernel and every Web Dispatcher together, then fix the gateway's proxy access list. Onapsis says it has not seen ICM2SHELL or PROXYGATE exploited, and BleepingComputer does not report exploitation of any of the four. BleepingComputer counts 35 vulnerabilities fixed in total this month.
The four 10.0 flaws
| CVE | Component | What an unauthenticated attacker gets | SAP Note |
|---|---|---|---|
| CVE-2026-76964 | ICM (NetWeaver AS ABAP) | Memory corruption, remote code execution | 3778530 |
| CVE-2026-89126 | SAP Web Dispatcher | Memory corruption, remote code execution | 3778556 |
| CVE-2026-89103 | SAP Gateway | Treated as one of the system's own application servers | 3798345 |
| CVE-2026-120017 | SAML 2.0 service provider (AS ABAP) | Log in as any user, including privileged ones | 3849308 |
The scores come from SAP's advisory as reported by The Hacker News and BleepingComputer; the SAP Notes themselves sit behind a customer login, and the note numbers above are as The Hacker News lists them.
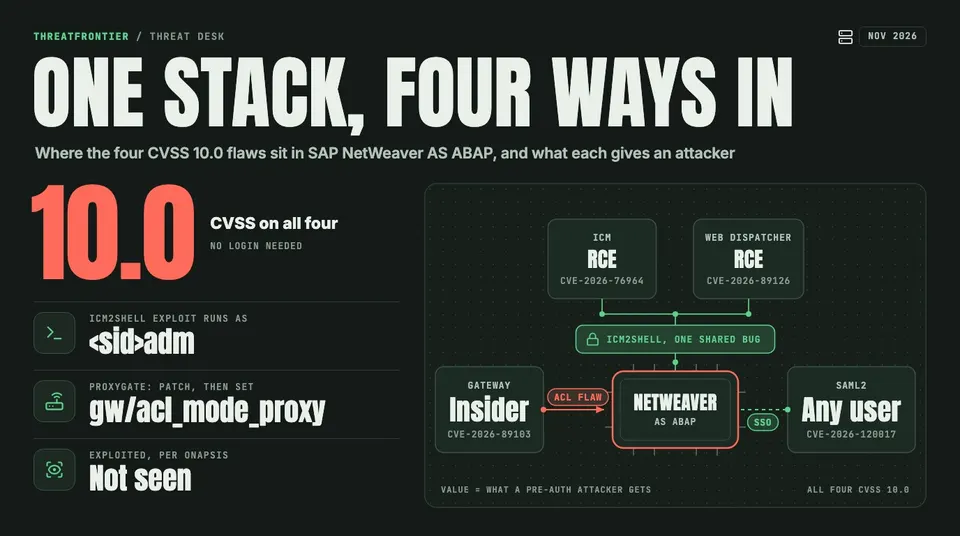
Where November's four CVSS 10.0 flaws sit in NetWeaver AS ABAP, and what each gives an attacker who has not logged in.
ICM2SHELL (CVE-2026-76964, CVE-2026-89126)
Onapsis says both CVEs come from one flaw in kernel code shared by ICM and the Web Dispatcher, used to reassemble WebSocket messages. The Hacker News quotes RedRays describing malformed WebSocket frames that trigger a heap out-of-bounds write before any authentication. Onapsis's exploit runs operating-system commands as <sid>adm. The same bug can also crash the Web Dispatcher, which cuts off access to the SAP systems it fronts.
WebSocket support is enabled by default, so a system is exposed even if no application uses it. AS Java is not affected; dual-stack systems are affected through their ABAP stack. The listed kernels are KERNEL 7.53, 7.54, 7.77, 7.93, 9.16, 9.18 and 9.20, plus KRNL64UC 7.53. Onapsis adds that out-of-maintenance kernels in the 7.40 to 7.89 range are also affected. The embedded Web Dispatchers in SAP HANA XS Classic and XS Advanced are in scope too.
PROXYGATE (CVE-2026-89103)
SAP Gateway uses access control lists to decide which hosts may connect to it and relay traffic. The flaw lets an external attacker be treated as one of the system's internal application servers. Exposure depends on the gateway's proxy list (prxyinfo) or, where that list is missing, the gw/acl_mode_proxy parameter, whose default of 0 allows every proxy connection.
The two outlets describe the impact differently. The Hacker News frames it as impersonation that lets the attacker carry out unauthorized actions. BleepingComputer, citing Onapsis, calls it a pre-authentication remote code execution bug that gives control of the system. Either way, the patch alone does not close it: the access list has to be fixed as well.
SAML2 bypass (CVE-2026-120017)
This is a missing-authentication flaw in the SAML 2.0 service provider of AS ABAP and ABAP Platform. SAP says an attacker could log in as any user, including privileged ones, on affected SAML single sign-on configurations. Affected releases are SAP_BASIS 702 through 758, 816, and 920 through 922. There is no workaround; the fix is the patch.
What to do
- Patch the kernel and every Web Dispatcher together. Inventory all instances, including the ones embedded in SAP HANA XS; one missed dispatcher leaves the hole open.
- Check the 7.93 patch level. On kernel 7.93, patch level 419 is still vulnerable. The fix is in the updated 401 Stack Kernel, 402, or 420 and later.
- Don't rely on the Web Dispatcher to shield ICM. Per SAP's FAQ note 3778788, as reported by The Hacker News, a patched dispatcher does not protect ICM if ICM ports are reachable directly or if the dispatcher runs as a router (PROT=ROUTER).
- Fix the gateway configuration. Restrict
prxyinfo, or setgw/acl_mode_proxyto 1 where no proxy list exists. Limit network access to gateway ports to the hosts that need RFC. - Last resort for ICM2SHELL: disable WebSocket support, after checking which applications rely on it.
- SAML: treat every AS ABAP system with SAML2 browser logon as in scope, review the trusted identity providers, and audit privileged SAML logons from unexpected sources.
Why this one matters
SAP has now shipped a maximum-severity fix in four consecutive months, per BleepingComputer: CVE-2026-58231 in August, CVE-2026-44756 (OVERPASS) in September, and CVE-2026-89111 in October, which TF covered in SAP Cloud SDK for Python OAuth2 SSRF Leads October Patch Day. October's patch day also fixed the NetWeaver Visual Composer flaw covered in SAP Patch Day: another critical 9.9 in NetWeaver Visual Composer.
CISA has flagged 14 SAP flaws as exploited since November 2021; TF covered one such chain in SAP Patches Second Critical NetWeaver Flaw After Researchers Link It to Chained Zero-Day Attacks. None of November's four is reported exploited yet, but a working exploit for ICM2SHELL already exists in a researcher's hands, and these bugs sit in the components that face the network first.